

#TeamGen malware analyst 🖖 (Norton, Avast, Lifelock, MoneyLion...) | Author of the book Ghidra Software Reverse Engineering for Beginners
Galicia, Spain
Joined January 2019
- Tweets2.3K
- Following692
- Followers677
- Likes3.9K





Pinned Tweet
🚀 Ghidra 12.2 released!
🔐Major server & TLS security changes
🛡️ZIP bomb protection + Server Allow List
🐍PyGhidra 3.2.0
⚡ Database & performance improvements
☕ Java 25 required
⬇️
github.com/NationalSecurityA…
#Ghidra #ReverseEngineering #CyberSecurity
🤖 Made with AI

David Álvarez retweeted

Cybersecurity is a team sport. As we wrap up #CybersecurityAwarenessMonth, remember: protecting our networks isn't just IT’s responsibility—it’s everyone’s. Let’s stay resilient together. #CyberAware #NSA #NationalSecurity
David Álvarez retweeted

As promised... teapaw.org/Farenain/status/211605…

This friday @yates82 @jeppojeps and I will release Dragon-tales, the tool I have used for doing the VMProtect analysis. The tool provides the next features:
Binary loading (ELF & PE/COFF), Disassembly & assembly (x86, ARM, RISC-V), CFG & function recovery, ...


David Álvarez retweeted
This friday @yates82 @jeppojeps and I will release Dragon-tales, the tool I have used for doing the VMProtect analysis. The tool provides the next features:
Binary loading (ELF & PE/COFF), Disassembly & assembly (x86, ARM, RISC-V), CFG & function recovery, ...
David Álvarez retweeted
I have done the second part of the analysis of VMProtect with Claude and Dragon-Tales, after the improvement I had after chatting with @k0mkc, and after @mr_phrazer & @nicolodev talk, I have gone deeper into Virtualization+Mutation, as well as discovering the GOT in the VM


David Álvarez retweeted
You can find the post here: farena.in/dragon-tales-web/p…
And here the resources: github.com/Fare9/Dragons-vs-…
The theory behind Dragon-Tales can be found in my trainings on LLVM Binary Analysis for @fuzzsociety_org do not hesitate asking to @jeppojeps about it!
CC @yates82
David Álvarez retweeted

Check this out, sounds like a huge progress. Scammers are going to go wild with this one:

We believe voice is the most natural way to interact with intelligence, so we created Dessa, the most authentic full-duplex speech model ever built. Talking with it feels like talking with a person…full of emotion, nuance, pauses, and a natural cadence.
block.xyz/dessa

David Álvarez retweeted

How Some Malicious AI Skills Hide Instructions from Human Reviewers
* Whitespace padding
* HTML comments
* Invisible Unicode
blog.virustotal.com/2026/10/…
David Álvarez retweeted

¡Ya están abiertas las inscripciones para #C3TF2026!

David Álvarez retweeted
VirusTotal is now available in ChatGPT
Scan files, URLs, and domains for potential threats, right from your chat
chatgpt.com/plugins/plugin_a…
David Álvarez retweeted

We've just published a technical breakdown of #WardenStealer, an actively developed MaaS #infostealer which, in just two months, already positioned itself as one of the most prevalent infostealers we protect our users from, ranking on par with Amatera, Remus and Vidar.
Warden is written in Rust🦀and ships with its own loader and a built-in crypto clipper, and its builds are heavily obfuscated, morphed, and regularly updated to evade detection.
It is also one of the first stealers to target configuration files and local data belonging to AI assistants and agentic coding tools.
Read the full technical breakdown ↓
gendigital.com/blog/insights…

David Álvarez retweeted
As I promised, Exploiting Reversing (ER) series: article 10 | iOS Security Research (part 01) is available on my blog now:
exploitreversing.com/2026/10…
The primary source for new articles is blackstormsecurity.com/resea…, but articles will continue to be published on my blog with a one-week delay.
Enjoy the reading and have an excellent day.
#iOS #VulnerabilityResearch #ExploitDevelopment #ReverseEngineering #KernelSecurity

David Álvarez retweeted
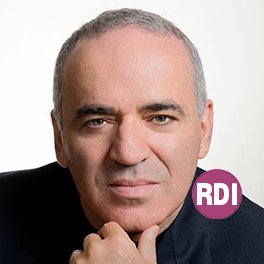
When the news broke about the Kremlin's threats against my life and the lives of my fellow dissidents, I was in Strasbourg petitioning the Parliamentary Assembly of the Council of Europe (PACE) and its European Court of Human Rights (ECHR). My colleagues and our allies at PACE are pursuing ways to oblige the use of frozen Russian funds as compensation for cases Russia lost at the court. By so doing, we seek to create the legal mechanisms to overcome the resistance in some European capitals, especially France and Belgium, to using these hundreds of billions to compensate and aid Ukraine, victim of countless Russian crimes against humanity.
But the current cases regarding Russian citizens are already substantial, over 3.3 billion Euros of unpaid awards owed by Russia from when it was a member of PACE. There should be no controversy and no delay in using the frozen funds to satisfy those awards. My thanks to PACE President Petra Bayr (photo) for her solidarity and leadership in this matter. Full story and link to the resolution:
facebook.com/share/p/18vGRig…


David Álvarez retweeted
The IDA 9.5 Beta is live!
◾ IDA MCP + Assist for agentic RE
◾ New TriCore, Hexagon and DEX/ODEX decompilers
◾ Recursive decompilation
◾ New Malware Analysis add-on
◾ And more...
Beta members: it's in your Download Center now.
Not in the Beta program? Join from the customer portal today.
hex-rays.com/blog/ida-9.5-be…

David Álvarez retweeted

putin’s desperate plot to silence Garry Kasparov on American soil.
putin’s regime has once again proven that it operates less like a legitimate government and more like a transnational mafia syndicate.
According to an explosive investigative report by the Spanish newspaper El Mundo, the Kremlin’s intelligence hit squads reached all the way into the United States in a cowardly attempt to murder legendary chess champion and fearless pro-democracy leader Garry Kasparov.
For years, @kasparov63 has used his massive global platform to speak truth to power, exposing the corruption, brutality, and lawlessness of putin’s dictatorship.
Unable to defeat his ideas with arguments, the Kremlin resorted to its default language: violence and terror.
U.S. authorities had to step in this summer to directly warn Garry Kasparov that he was a top target for Kremlin assassins, forcing official security measures to shield his life. This wasn't just a vague threat. Court documents and investigative reports reveal a chilling network of operatives hunting anti-putin voices across borders.
While putin’s thugs tried to outsource their dirty work, offering pocket change to mercenaries to stalk targets in Washington, the plot exposes the utter panic inside the Kremlin.
Dictators like putin are terrified of brilliant, uncompromised voices like Kasparov who remind the world that a free, democratic Russia is possible.
This assassination plot shatters the illusion that critics are safe once they leave Russia.
Yet, for all their dark money, surveillance networks, and hired thugs, the Kremlin's desperation only reveals their weakness. They can threaten, stalk, and plot, but they will never silence Garry Kasparov, nor the unstoppable demand for freedom.

David Álvarez retweeted
I responded in more detail in The Next Move here, and there will be more tomorrow from Strasbourg, where we are moving forward to make Russia pay, literally, for its evil. thenextmove.org/p/new-detail…

David Álvarez retweeted

Your AI agent is safe. Says who?
New claims like this land every day. Verifying them is a different story. So we at @GenDigitalInc drove an @AMTSO working group on independent testing of AI agent security. Labs and vendors at one table, so the next time someone says "it's safe", there is a way to check.
gendigital.com/blog/insights…

David Álvarez retweeted
The 13th Annual NSA Codebreaker Challenge is LIVE! Join the mission and test your cybersecurity skills. Visit nsa-codebreaker.org to register and start your first phase today! #CodebreakerChallenge


David Álvarez retweeted

HyperDbg v0.24 is released!
It includes nine new commands, support for arrays as function parameters, char and wide-char arrays, fix kernel-mode builds on Linux, plus major bug fixes and refactoring.
Check it out:
github.com/HyperDbg/HyperDbg…
