

Pernah cuba tanam ciku, tapi tak berbuah (CC BY 4.0)
Malaysia
Joined July 2009
- Tweets2.8K
- Following788
- Followers4.6K
- Likes0




Pinned Tweet
Fake Base Transceiver Station atau Fake BTS adalah sebuah peranti yang menyamar sebagai stesen pangkalan telefon bimbit sebenar. Di Malaysia, ia selalunya bertujuan untuk menyebarkan SMS phishing. Lagi best, nama penghantar SMS pun boleh di spoof!


Adnan (xanda) Mohd Shukor retweeted

Parallel Pulse 2026, wrapped!
After months of planning, conversations, ideas and work behind the scenes, Parallel Pulse 2026 came together on 28 September at AICB, Kuala Lumpur.
And what a day it was.
We started with an idea. The community made it real.
Until the next one ⚡


Adnan (xanda) Mohd Shukor retweeted
𝗧𝗵𝗲 𝗩𝗶𝗹𝗹𝗮𝗴𝗲𝘀 𝗼𝗳 #ParallelPulse2026
🧩 SherpaSec Cybersecurity Escape Room
🤖 AI Security Village by U9up
🏁 RAG CTF by Hackami
Which village are you taking on first? 👀
#CyberSecurity #KancilResearchLabs #NanoSec #SIAGAInformatics

Adnan (xanda) Mohd Shukor retweeted
In 𝗹𝗲𝘀𝘀 𝘁𝗵𝗮𝗻 𝟮𝟰 𝗵𝗼𝘂𝗿𝘀, #ParallelPulse2026 registration will CLOSE!
Get your tickets: tickets.nanosec.asia/nanosec……
Regular: RM188
Students: RM88
📅 28th September 2026
⏰ 9am - 6pm
📍 AICB, Kuala Lumpur
See you there!
#CyberSecurity #NanoSec #SIAGAInformatics

Adnan (xanda) Mohd Shukor retweeted
𝗠𝗲𝗲𝘁 𝘁𝗵𝗲 𝘃𝗼𝗶𝗰𝗲𝘀 𝗼𝗳 𝗣𝗮𝗿𝗮𝗹𝗹𝗲𝗹 𝗣𝘂𝗹𝘀𝗲 𝟮𝟬𝟮𝟲!
📅 28 September 2026
📍 AICB, Kuala Lumpur
Registration opens until 12am, 24th September 2026
tickets.nanosec.asia/nanosec…
See you at #ParallelPulse2026! ⚡
#NanoSec #SIAGAInformatics #TechEvents2026

Adnan (xanda) Mohd Shukor retweeted
𝟱 𝗱𝗮𝘆𝘀 𝗹𝗲𝗳𝘁 to register for #ParallelPulse2026
🎟️ Registration closes on the 𝟮𝟰𝘁𝗵 𝗼𝗳 𝗦𝗲𝗽𝘁𝗲𝗺𝗯𝗲𝗿 𝟮𝟬𝟮𝟲, 𝟭𝟮.𝟬𝟬𝗮𝗺
Secure your spot here:
tickets.nanosec.asia/nanosec…
#CyberSecurity #AISecurity #DFIR #CyberCommunity #NanoSec #SIAGAInformatics
Man drove around Singapore with 'SMS blaster' that sent more than 10,000 phishing messages, gets jail
channelnewsasia.com/singapor…

Adnan (xanda) Mohd Shukor retweeted

macam biasa, dia je takda buat jahat

We're publishing our most detailed threat intelligence report to date.
It covers how people tried to misuse Claude—for cyberattacks, influence operations, surveillance, biology, and building weapons—and how we found and stopped them.
We disrupted every operation in the report, and used the lessons from them to strengthen our safeguards. Where appropriate, we also shared what we found with authorities and other AI companies.
These cases are not typical: we’re highlighting some of the most sophisticated misuse we’ve seen. But they’re especially important to discuss, because they show us where AI misuse is headed, where our safeguards work, and where they need to improve.
We’re publishing this report so others can spot the same activity on their own platforms, and so we can give the public a clearer view of how emerging threats develop.
Read the report: anthropic.com/threat-intelli…

Adnan (xanda) Mohd Shukor retweeted

✍️ An Awesome Series of Writeups on Anti-DDoS research
Part 1: cocomelonc.github.io/linux/2…
Part 2: cocomelonc.github.io/linux/2…
Part 3: cocomelonc.github.io/linux/2…
Part 4: cocomelonc.github.io/linux/2…
Author: @cocomelonckz


Threat actor SilverFox is hiding malware inside ISO/IMG files and compressed into zip file. When opened, Windows auto-mounts the image as a virtual CD-ROM, bypassing MotW/perimeter controls to deliver the malicious payloads
Adnan (xanda) Mohd Shukor retweeted
Suspicious incoming calls are now flagged with a “Suspected Scam” alert on customers’ phones.
thestar.com.my/tech/tech-new…


Scammers are shifting to messaging services such as Rich Communication Services (RCS) and iMessage to spread phishing links following the enforcement of hyperlink restrictions on short messaging service (SMS).
thestar.com.my/news/nation/2…

Adnan (xanda) Mohd Shukor retweeted

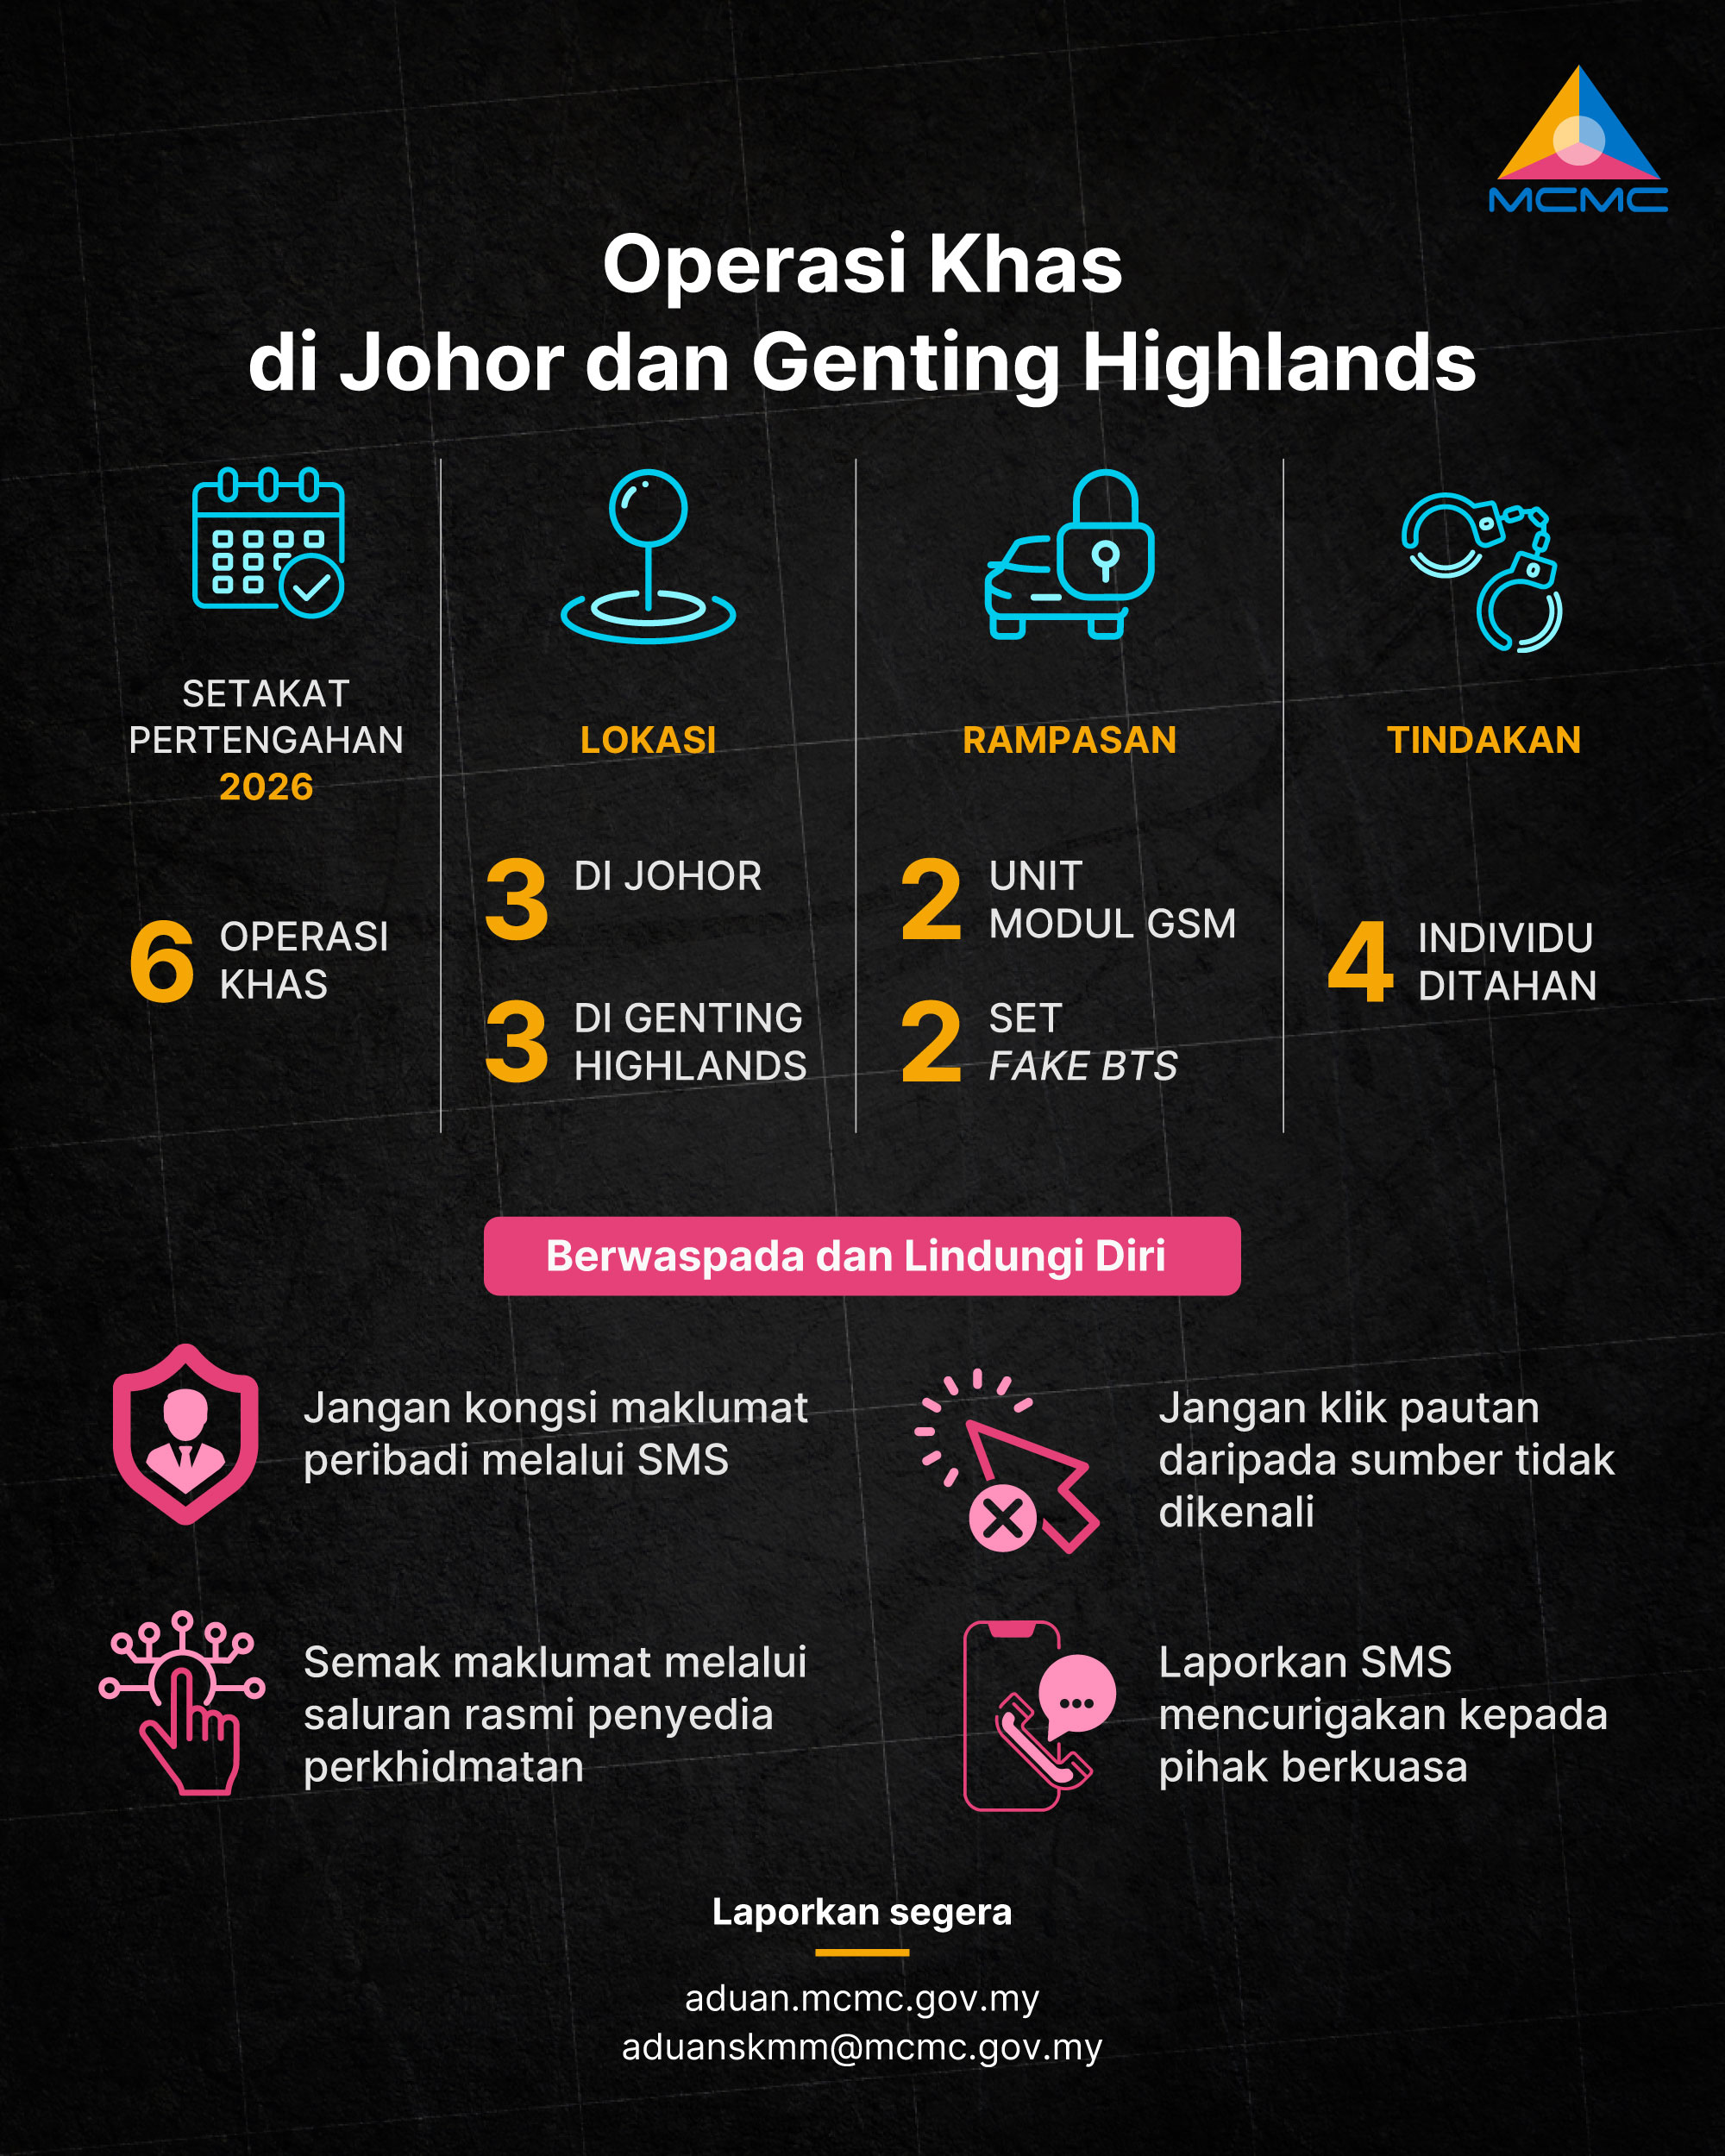
Lindungi diri anda daripada menjadi mangsa:
• Jangan kongsi maklumat peribadi melalui SMS.
• Jangan klik pautan daripada sumber yang tidak dikenali.
• Semak kesahihan maklumat melalui saluran rasmi penyedia perkhidmatan.
• Laporkan SMS yang mencurigakan.

Adnan (xanda) Mohd Shukor retweeted

MCMC Busts Syndicate Using Fake BTS to Send Fraudulent SMS
The technology allows fraudulent messages to appear as if they were sent by a legitimate party, increasing the risk of users being misled by the included web links
Read more
theiskandarian.com/mcmc-bust…

Adnan (xanda) Mohd Shukor retweeted

Malaysian Regulator Stops SMS Blaster Bypassing Telco Filters - commsrisk.com/malaysian-regu…
MCMC found a 23 year old man driving around Johor Bahru with an SMS blaster that sent scam links. This was its fifth special operation against the devices during 2026.

We've observed an increase of compromised Malaysian websites displaying fake CAPTCHA pages that instruct users to press Win + R, paste a command, and run it.
⚠️ This is NOT a CAPTCHA. It installs malware.
✅ Legitimate CAPTCHA will NEVER ask you to copy and run commands.


Lelaki asing dicekup di Miri, disyaki pasang alat 'skimming' ATM di Brunei
bharian.com.my/berita/kes/20…
