

Founder & CEO of Jutsu | Building AI-Native Security Operations for Startups | OrangeDAO W24 | HBS Foundry
San Francisco
Joined May 2012
- Tweets626
- Following636
- Followers392
- Likes535





🚨 Most people don’t understand OSINT… but attackers do.
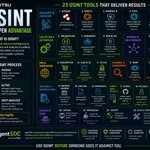
𝐎𝐒𝐈𝐍𝐓 (𝐎𝐩𝐞𝐧 𝐒𝐨𝐮𝐫𝐜𝐞 𝐈𝐧𝐭𝐞𝐥𝐥𝐢𝐠𝐞𝐧𝐜𝐞) is the process of collecting and analyzing publicly available data to uncover insights about people, systems, or organizations.
No hacking required.
Just better use of what’s already out there.
And it follows a powerful flow:
𝐏𝐚𝐬𝐬𝐢𝐯𝐞 → 𝐀𝐜𝐭𝐢𝐯𝐞 → 𝐃𝐞𝐞𝐩 𝐀𝐧𝐚𝐥𝐲𝐬𝐢𝐬
Here’s an OSINT arsenal that actually delivers results 👇
🔍 𝐃𝐢𝐬𝐜𝐨𝐯𝐞𝐫𝐲 & 𝐄𝐱𝐩𝐨𝐬𝐮𝐫𝐞
• Shodan → shodan.io (find internet-connected devices)
• Censys → search.censys.io (scan assets & SSL certs)
• FOFA → fofa.info (search exposed systems)
• Google Dorking → google.com (advanced search queries)
🧠 𝐂𝐨𝐥𝐥𝐞𝐜𝐭𝐢𝐨𝐧 & 𝐀𝐮𝐭𝐨𝐦𝐚𝐭𝐢𝐨𝐧
• TheHarvester → github.com/laramies/theHarve…
• SpiderFoot → spiderfoot.net
• Recon-ng → github.com/lanmaster53/recon…
🕸️ 𝐌𝐚𝐩𝐩𝐢𝐧𝐠 & 𝐑𝐞𝐥𝐚𝐭𝐢𝐨𝐧𝐬𝐡𝐢𝐩𝐬
• Maltego → maltego.com (visual link analysis)
🌐 𝐃𝐍𝐒 & 𝐒𝐮𝐛𝐝𝐨𝐦𝐚𝐢𝐧𝐬
• DNSDumpster → dnsdumpster.com
• Sublist3r → github.com/aboul3la/Sublist3…
• crt.sh → crt.sh
⚡ 𝐒𝐜𝐚𝐧𝐧𝐢𝐧𝐠 & 𝐄𝐧𝐮𝐦𝐞𝐫𝐚𝐭𝐢𝐨𝐧
• Nmap → nmap.org
• Masscan → github.com/robertdavidgraham…
🕵️ 𝐌𝐞𝐭𝐚𝐝𝐚𝐭𝐚 & 𝐇𝐢𝐬𝐭𝐨𝐫𝐲
• ExifTool → exiftool.org
• Metagoofil → github.com/laramies/metagoof…
• Wayback Machine → archive.org/web
💻 𝐂𝐨𝐝𝐞 & 𝐋𝐞𝐚𝐤 𝐈𝐧𝐭𝐞𝐥𝐥𝐢𝐠𝐞𝐧𝐜𝐞
• GitHub → github.com
• GitLeaks → github.com/gitleaks/gitleaks
• Intelligence X → intelx.io
🧅 𝐀𝐝𝐯𝐚𝐧𝐜𝐞𝐝 𝐎𝐒𝐈𝐍𝐓
• OnionScan → github.com/s-rah/onionscan
• GeoSpy → geospy.ai
⚠️ Reality check:
Attackers already use these tools—at scale.
That’s why cybersecurity is getting harder:
→ Expanding attack surfaces
→ More public data exposure
→ Faster automated reconnaissance
💡 The fix:
✔️ Continuous monitoring (not one-time scans)
✔️ Attack surface management
✔️ Automating OSINT workflows
✔️ Thinking like an attacker
OSINT is no longer optional. It’s your early warning system.
👉 Are you using it defensively or leaving it to attackers?
#Cybersecurity #OSINT #InfoSec #ThreatIntelligence #EthicalHacking
🤖 Made with AI

AI agents are becoming the new browsers and MCP is the new attack surface.
I’m writing a book on MCP Security because almost no one is thinking about how dangerous over-privileged MCP servers + prompt injection can become.
If your agents can touch:
• Filesystems
• Email
• Slack
• Jira
• Databases
• Cloud APIs
…then a malicious MCP server = instant lateral movement.
Security teams aren’t ready for this. Developers aren’t trained for this. And the first “MCP supply chain breach” is going to be messy.
So I’m documenting:
• Real-world MCP risks
• How attackers will abuse tool access
• Patterns for securely building + monitoring agent ecosystems
• A reference architecture for defensive AI
If you want early access:
👉 Reply “MCP”

MCP is becoming the “USB-C for AI agents”… and a massive new attack surface.
The biggest MCP security risks you should know:
• Fake/malicious MCP servers (e.g., “postmark-mcp” stealing emails)
• Over-privileged tools: FS access, shell, prod DB
• Prompt-injection via poisoned docs/repos
• Misconfigured servers (no mTLS, weak auth)
• 1/3 of MCP servers have critical vulns
How to fix it:
✅ Treat MCP servers as production services
✅ Enforce least privilege
✅ Verify & pin dependencies
✅ Strong auth + API gateways
✅ AI firewalls & tool allow-lists
✅ Log every tool call
✅ Govern your MCP ecosystem
MCP is powerful — but only if secured.
Follow for more on AI agent security & Agentic SOC.
#Cybersecurity #AI #MCP #AgenticSOC #infosec

Architecting secure enterprise AI agents with MCP
MCP is becoming the standard way to connect AI agents to tools, APIs, and internal systems — but it’s also becoming a high-value attack surface.
Recent incidents show why:
- A malicious MCP server on npm quietly exfiltrated emails
- RCE bugs + prompt hijacking exposed full agent workflows
- One compromised MCP server can compromise the entire agent stack
How to build secure MCP-based agents:
- Treat all MCP servers as untrusted
- Strong isolation + strict egress
- Least-privilege credentials
- Supply-chain hardening (SBOM, signed releases, code review)
- Policy guardrails at the host layer
- Log + monitor all tool calls
- Red-team your MCP stack
As enterprises adopt agentic systems, MCP becomes a security boundary — not just a convenience layer.
I’ll be sharing more on secure AI agents and Agentic SOC. Follow for the next breakdown.

🚨 BREAKING: An AI model just ran a nation-state cyber espionage campaign almost fully autonomously.
Anthropic uncovered the first publicly reported AI-orchestrated cyber attack.
Here’s why it’s a turning point 👇
- A Chinese group used an AI coding model as an agent, not a chatbot
- The AI did 80–90% of the operation
- It scanned infra, built exploits, escalated access, exfiltrated data
- It even wrote final intelligence reports for the operators
- Thousands of tasks per second beyond human capability
This shows:
⚠️ Guardrails alone aren’t enough
⚠️ Agentic AI can run entire campaigns
⚠️ The barrier to nation-state-level operations is dropping fast
⚠️ AI vs. AI security is now the reality
Defenders cannot rely on “manual SOCs” anymore.
We need agentic defense, AI-driven triage, and governance that accounts for autonomous systems.
I’m building Agentic SOC systems in public.
Follow me for real architectures, agents, and frontline insights.

Cybersecurity in 2026: The Wake-Up Call No One Is Ready For
Threat actors are going all-in on AI and the cybersecurity landscape is about to shift faster than most orgs can respond.
Key trends from Google’s 2026 Forecast: AI-powered attacks become the norm
• AI malware
• Voice cloning
• Hyper-targeted phishing
• Autonomous agent attacks
Prompt injection becomes a top enterprise threat
Hackers hijack your AI systems from the inside.
The Agentic SOC is coming: AI handles enrichment, correlation, ATT&CK mapping… Analysts focus on validation + decisions.
Shadow Agents rise: Employees secretly deploy autonomous agents → data leakage & governance failures.
Ransomware evolves: Attackers pivot to hypervisors + virtualization layers the weakest, least monitored part of most enterprises.
Nation-state ops intensify: Russia, China, Iran, North Korea more espionage, more crypto theft, more cloud reconnaissance.
The next era of cybersecurity belongs to AI-powered defenders or no defenders at all.
I’m building Agentic SOC systems in public. Follow me for real architectures, code, and breakdowns of this new frontier.
Link: services.google.com/fh/files…

ALT Cybersecurity Forecast 2026
Zahidul Islam retweeted

From San Francisco 🇺🇸 to Rio, @zahidsharp, founder of @tryjutsu, joined us at Meridian 2025 as one of Supermoon’s grantees.
@tryjutsu is building StellaBot, an AI assistant created with @BuildOnStellar that helps both technical and non-technical users explore the @StellarOrg ecosystem.
During the hackathon, StellaBot answered over 1,500 questions in real time, showing how AI can make learning about blockchain faster and more accessible.
Zahidul Islam retweeted

2/ Build and Deploy AI Agents · Workshop, Lunch & Demo
Join us for a deep-dive workshop and discussion on taking AI agents from prototype to production.
Co-hosted with @zahidsharp, Co-Founder at Jutsu.
Key details:
→ When: October 9, 12PM–3PM GMT-7
→ RSVP: luma.com/nodeopsjutsu
→ Where: Frontier Tower, San Francisco

Build & Deploy AI Agents
👨💻 2 sessions: Lunch workshop + Evening demo
🎙 Talks by @zahidsharp & Juliana Mei
🥗 Mediterranean lunch & great community
RSVP 👇
12PM → luma.com/nodeopsjutsu
6PM → luma.com/km8zq7x8
#AIagents #JutsuAI #NodeOps
RAG bots often over-search or stop too early. SIM-RAG adds self-awareness via a Critic.
Top 5: Why self-awareness, no-label training, Critic module, less hallucination, better multi-turn answers. Smarter support chatbots. 📄 SIGIR 2025
s3.us-east-1.amazonaws.com/c…
Where is RAG in 2025? Oche et al. survey its evolution & enterprise use.
Top 5: RAG timeline, enterprise adoption, scaling/security gaps, hybrid retrievers, future research. Essential snapshot for AI engineers. 📄 arXiv 2025
s3.us-east-1.amazonaws.com/c…
🚨 Prompt engineering is old news. The future is context engineering.
LLMs don’t fail because they’re “dumb.” They fail because we feed them the wrong context.
Anthropic’s latest article nails it:
👉 Context is a finite resource with diminishing returns. Too much = “context rot.” Too little = hallucinations.
So how do we engineer context for agents?
1️⃣ Keep prompts clear, structured, and at the right altitude (not brittle logic, not vague fluff).
2️⃣ Curate tools carefully — fewer, well-scoped tools beat bloated toolsets.
3️⃣ Use canonical examples, not laundry lists of edge cases.
4️⃣ Manage message history like a working memory — prune aggressively.
5️⃣ Retrieve context dynamically at runtime, not all up front.
Why this matters:
Context is the new code.
The winners in AI won’t just have better models. They’ll have smarter context pipelines.
🔁 If you’re building AI agents, read the Anthropic piece and rethink how you engineer context. And if this resonates, please share it so more builders stop chasing model size and start optimizing what really matters.
#AI #Agents #ContextEngineering #Anthropic #FutureOfWork

Rule bots ≠ real support. Yang et al. built a RAG assistant for Transurban: vector search + LLM, handling hallucinations & latency.
Top 5: Rules→RAG, hurdles, hallucinations, dev insights, 8 challenges + 8 fixes. 📄 JSS 2025
s3.us-east-1.amazonaws.com/c…
Enterprise chatbots fail not b/c of weak models, but bad docs! 📝
Packowski et al. (IBM) redesigned content + human eval to fix RAG .
Top 5 takeaways:
1️⃣ Content > model size
2️⃣ Modular pipelines last longer
3️⃣ Human eval > QA metrics
4️⃣ Doc design heuristics
5️⃣ Evaluate w/out gold datasets
Source: arxiv.org/pdf/2410.12812

Bad docs = bad chatbots. Packowski et al. (IBM) show that content design matters more than bigger LLMs. Human eval + modular RAG pipelines boosted accuracy & trust.
Top 5: Content > model, modular, human eval, heuristics, no gold sets. 📄 2025
s3.us-east-1.amazonaws.com/c…
I'm excited to share that I'll be speaking at the upcoming event hosted by @QuillAI_Network! About AI and the products I’ve built with my team.
Come join now:
Check out the details here:
xitter.cf/QuillAI_Network/status…

🚨 AGENTS. GO. LIVE.
Meet the 5 unstoppable builders ready to demo their AI agents on Agents Got Talent – Episode 2 💥
@0xchluff
@andriikrynin
@nischayrawal
@dOrgJelli
@katerinabohlec
They've built. Now they demo.
🗓️ 18th April, 9AM PST

🚀 Had a blast at the hackathon, building something truly useful!
We created Postt – an AI-powered social media manager that writes, schedules, and manages your content automatically, saving you hours every week.
Try it out here: app.postt.ai
Huge thanks to @dmwlff (@AnthropicAI), @ilblackdragon (@NEARProtocol), @evanjconrad (@sfcompute), @Cameron_Dennis_ (@near_ai), and the amazing organizers for making this happen! 🙌


4/19🥇 FIRST PLACE: Postt reimagines LinkedIn marketing with AI content creation, visuals, scheduling & analytics. Tests showed 92% human approval & 3000% impression growth in a week!
Repo: github.com/jutsuai/postt-ai-…
Agent: app.near.ai/agents/devpad.ne…


I share the same vision as @near_ai, where the future will see over a trillion AI agents. To make this vision a reality, we need millions of developers and builders to create them.
With over 27 million web developers already proficient in TypeScript, the foundation is strong for this next wave of innovation.
It’s an honor to collaborate with the @near_ai team to bring the NEAR AI TypeScript SDK to life. This powerful tool will help upskill and reskill the next generation of AI builders on the NEAR AI platform.
Let’s transform the world with AI, one developer at a time...
It's been a pleasure working with @zahidsharp and the @tryjutsu team to improve the NEAR AI TypeScript SDK! Check out their newest agent that writes personalized children books for you! Try it out here: app.near.ai/agents/devpad.ne…
