

Shipping apps in public. Real traffic, real bugs and the fixes, from @onehausapp + @mcpscores. Plus dev tips I'd want someone to tell me
London, England
Joined July 2016
- Tweets3.9K
- Following1.5K
- Followers1.3K
- Likes2.7K




CodeWithStu retweeted

I honestly can't remember another week quite like October 14–21 in software security.
Just between October 14 and October 21:
- Next.js patched two critical RCE vulnerabilities (9.5/10).
- NGINX patched five security vulnerabilities.
- PHP disclosed critical RCE vulnerabilities. AWS observed exploitation attempts four days before disclosure.
- Node.js patched multiple vulnerabilities, including potential RCE and TLS validation bypasses.
- GitLab disclosed another 10/10 vulnerability allowing potential unauthenticated RCE.
- LiteLLM's compromised releases distributed credential-stealing malware.
- Railway disclosed a potential exposure of customer secrets and API keys.
- OpenCode reported a breach affecting 1.4% of its Console users.
- eMudhra had eight trivially recoverable certificate authority private keys. One of them was literally the number 4!
Also, Microsoft reported AI-orchestrated attacks targeting over 2,250 Microsoft 365 tenants, with attackers obtaining privileged access in under three hours in multiple cases.
CrowdStrike documented AI agents conducting real-world intrusions, including one that obtained domain-controller credentials in approximately 20 minutes without further human guidance.
Meanwhile, Cloudflare observed PHP exploitation attempts growing to millions within hours of disclosure. Some of the attacks even started before any public disclosure, which shows that malicious actors have ways to get to the important information way before any organization does.
All of this obviously made me think about what this means for engineering organizations.
For years, we've treated vulnerability management as something that happens periodically. We review advisories, create tickets, plan upgrades, and eventually deploy patches. Sometimes days later, sometimes weeks, and quite often months or even years.
That's not going to work anymore and technical decision-makers will need to fundamentally rethink how their organizations approach security.
Continuous monitoring, immediate exposure assessment, automated mitigation, credential rotation, and rapid patching need to become standard engineering capabilities.
We need to start measuring our security response times in minutes, not days, weeks, months, or years.
CodeWithStu retweeted

As of 20 Oct the official MCP registry has about 48,000 servers, and the median trust score across them is 65/100. Only around 1,800 score 90 or above.
It's also growing by roughly 600 to 700 new servers a day at the moment, which is a lot for anyone to vet by hand
CodeWithStu retweeted

ICYMI: For the 10th anniversary of "Site Reliability Engineering", we’ve rewritten the definitive Google SRE book! 📖
Featuring brand-new guidance on SRE for the agentic era, modern SLOs, and culture.
Get your copy today: goo.gle/SREbook

CodeWithStu retweeted

New on our Engineering blog: Creating in-house source control.
In May, we merged around 2,500 code changes per day. In September, we merged more than 30,000 per day. As a result, we became bottlenecked by developer infrastructure built for human (rather than agent) scale.
Here, we share how we built a new version control system—and fully migrated our monorepo from git—in five months: anthropic.com/engineering/re…

CodeWithStu retweeted

Connector submissions for @Muse are open 🚀
If you have MCP go here -> muse.ai/platform and submit ASAP


CodeWithStu retweeted

Giving away a free app audit every day!
I’m new here, so this is my way of getting to know you and giving something back.
Every day I’ll roast an app: onboarding + paywall, where the magic (money) happens. 💸
Drop your App Store link below and I’ll tell you what I’d fix first.

CodeWithStu retweeted

I’m looking for my next role.
If anyone knows of companies that have C#/.NET roles, let me know
I've spent the last few years working on Developer Tools that use the .NET Profiling APIs
My blog gives a good idea of my interests and skills mattwarren.org/
CodeWithStu retweeted

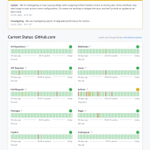
On August 17, GitHub experienced a significant outage that disrupted developers and organizations around the world. If you were trying to ship software that day, we let you down.
I posted in March and April about the steps we’re taking to make GitHub more reliable. The work is still underway. Here is an update:
github.blog/news-insights/co…

CodeWithStu retweeted

The RCA for the outage we had at GitHub yesterday is live.
We're sorry it happened and hope this answers your questions about it. The team is already working on the actions listed here to fix it.
githubstatus.com/incidents/z…

CodeWithStu retweeted

You might find this interesting:
xitter.cf/MrPeterLMorris/status/…
CodeWithStu retweeted

MCP 2026-07-28 is live and it's the largest update to the protocol since launch.
MCP is now stateless, making it easier to deploy and scale remote servers.
claude.com/blog/bringing-mcp…

CodeWithStu retweeted

(1) Today we're releasing Muse Spark 1.1 -- a strong agentic and coding model at a very low price. It's available through our new Meta Model API and in Meta AI.

CodeWithStu retweeted
I launched a thing! 🚀🚀🚀
OneHaus manages all of your tasks, remembers when your MOT is due and helps you remember without you asking it. Share the load across your house, not in one persons head.
You can try it for free today from the link below, available on iOS and web

CodeWithStu retweeted

Meet Gemma 4 12B!
A unified, encoder-free multimodal model designed to bring high-performance intelligence directly to your laptop, and released under an Apache 2.0 license.
Bridging the gap between edge efficiency and advanced reasoning. Here is what’s new with Gemma 4 12B: 👇

CodeWithStu retweeted

BLOG: WSL 2 is getting faster Windows file system access boxofcables.dev/wsl2-per-dev…

CodeWithStu retweeted

London has OFFICIALLY overtaken Paris to become Europe's leading tech hub! 🇬🇧
@dealroomco has just released its latest Tech Ecosystem Index, where it ranks tech hubs based on its growth, scale and density.
Last year Paris took the number one position.
Now London has taken it back.
The UK capital’s return to the top spot is driven by record AI investment - $7bn in 2025, as well as being home to 138 unicorns, including Wayve, Granola, OLIX and ElevenLabs.
This year the UK has continued to fly and has attracted 48% of all European Venture capital.
Amazing news for London, and a great report as always from @yoramdw, @smorla, @sabben and the team (link in comments).