

Combat veteran, OGA veteran, INFOSEC professional, firearms & tactics instructor. Creator of the GroundRod tradecraft courses. Follower of Christ
NW
Joined July 2024
- Tweets15.7K
- Following1.5K
- Followers4.4K
- Likes24.9K


K CSG retweeted

‼️ An encrypted USB drive from SecZure has a backdoor that opens its files without the user's password.
Two built-in accounts with fixed passwords decrypt them, Binary Ninja's Xusheng Li found.
OpenAI's Codex broke Netac's FileLock in 7 minutes and saw it logging passwords.


K CSG retweeted

🚨 HOLY SMOKES. A senior Army nuclear scientist who oversaw our NUCLEAR arsenal has been placed on leave by Sec. Hegseth, and could face CRIMINAL prosecution after being EXPOSED BY James O'Keefe
He is accused of divulging NUCLEAR SECRETS and MISSILE locations. Wow.
"Two segments of the video apparently capture Hugg disclosing to his young female interlocutor at least 4 locations of underground nuclear missiles and critical aspects of the launch process under which they could be fired off in the event of a nuclear conflict."
"Hugg appears to divulge classified information in a range of areas from ongoing use of nerve agents to war planning in Iran."
Great work @JamesOKeefeIII!
K CSG retweeted

What if a Signal-based messenger made privacy protections mandatory instead of optional?
Meet Parakeet, an open-source Android fork of Molly, itself based on Signal.
It takes a different approach to privacy:
🔹Tor via Orbot is mandatory and cannot be disabled in the app.
🔹Screenshots and app-switcher previews are blocked.
🔹Disappearing messages default to 24 hours for new chats.
🔹No Firebase Cloud Messaging (FCM) notification delivery.
🔹A redesigned interface and a separate app identity.
Parakeet tracks Molly's releases and reapplies its own changes automatically. The latest release listed includes an APK named Parakeet-8.19.2-4.apk.
Installation is available through the project's release page, with tools like Obtainium or Omnify Beta as an option.
Would you use a messenger that forces all traffic through Tor?
gitlab.com/LionNest/parakeet
#Privacy #OpenSource #Android #Signal

K CSG retweeted

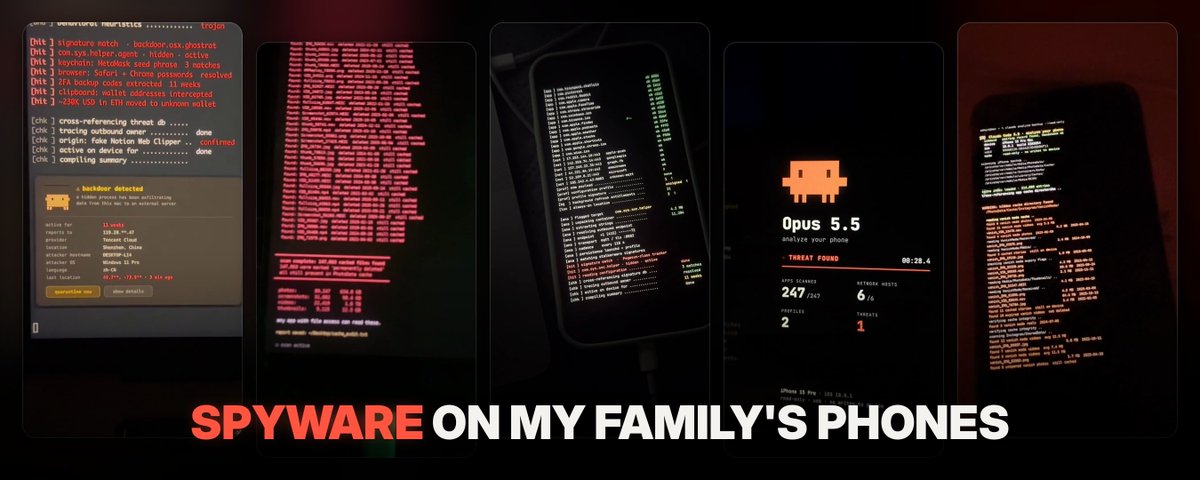
Claude Code found my wife's private photos and videos on 3 websites she never uploaded to. then it found a hidden app on my 13 year old daughter's phone sending her entire camera roll to a server every 6 hours. both found in the same scan.
someone sent my wife a link to a site she'd never heard of. her photos and videos were there. original files from her camera roll that were only ever on her phone.
i connected her iPhone to my MacBook and ran Claude Code. it found an active iCloud session logged in since March 2023.
IP → 116.25.***.91
location → Guangzhou, China
device → Windows 10 Pro
last sync → 6 hours ago
recovery email → x*****[email protected]
someone got her Apple ID from a leaked database and synced her entire library for over a year. she changed her password twice. they had a recovery email she never set up and got back in every time.
found on:
→ www.l**k-vault cc
→ www ph***dump to
→ telegram → t me/le***vault_asia (14,000+ subscribers)
the last thing Claude Code pulled from her account was photos and videos of our daughter. that made me check her phone next.
she's 13. she had a photo editor app with 2.7 million downloads from the App Store. Claude Code found it uploading her camera roll to a server in Vietnam every 6 hours.
server → 103.56.***.12
location → Ho Chi Minh City, Vietnam
total uploaded → 11,400 files
access → camera, photos, location, microphone
her face, her school, her friends, her exact location every day for 8 months. Apple approved the app. it's still live right now.
what we did that night:
→ killed the iCloud session and removed the recovery email
→ changed every password from my phone, not from hers
→ deleted the app and revoked every unnecessary permission on both phones
→ filed DMCA takedowns on all 3 sites
2 of the 3 sites took the content down. the telegram channel is still up.
my wife cried. my daughter still thinks i deleted her app because it was using too much battery. i'm not going to tell her the real reason.
the full step by step is below. takes 3 minutes. run it on every phone in your house tonight. save it so you don't lose it and send it to anyone with a family.

K CSG retweeted

Canadian internet users may soon have their data handed to US authorities, with no Canadian judge involved and no Canadian court order required.
That is the core of what Bill C-22 enables. Canada is negotiating a cross-border data-sharing agreement with the US that lets American law enforcement request information about Canadians directly from service providers, bypassing Canadian judicial oversight entirely.
And it does not stop there. C-22 also lets the Minister of Public Safety order companies to build encryption backdoors, and mandates that telecom and messaging platforms retain your metadata for up to a year, regardless of whether you are under any suspicion.
Is this not a sovereignty problem? A country that cannot protect its own citizens' digital lives from foreign law enforcement is not in control of its internet.
The bill has passed the House and is now in the Senate. The window to push back is closing fast.
If you are Canadian, the Canadian Civil Liberties Association has a petition. Use it please before it's too late.
K CSG retweeted

🚨Update: Massive Power Outage Coming! War Department prepares major U.S. milıtary bases to operate for 90 days without outside support, including civilian power grids and global supply chains!
- Fox News

K CSG retweeted

DJI is mass rolling out 1280 x 1024 thermal imaging for its Mavic-sized drones while American 640 x 480 imagers are on 6+ mo lead times
This should be a MASSIVE wake up call to the Western industrial base, fire alarms should be ringing.

K CSG retweeted

Target got caught raising prices on shoppers just for walking into its stores.
Now its baskets carry a Bluetooth tracker.
That tracker talks to Target's ceiling lights, over 2 million of them linked to its app.
With the Target app on your phone, the basket's path can be tied to you.
In People v. Target Corporation, a 2022 California judgment bars Target's app from raising prices "solely based on a user's geographic location."
KARE 11 found the same 10 items cost $262 more inside the store than in its parking lot.
It's bigger than Target.
Three states have already banned grocery prices built on your personal data.
You can't switch off the basket's tracker. But look the item up on Target.com before you pay. If it's cheaper there, Target will match it, even 14 days after you buy.
🎩 Kash Khan
da.venturacounty.gov/wp-cont…

K CSG retweeted

Muchos mensajes, análisis y comentarios como este, asegurando que las pandillas de Haití no son como las de El Salvador; que son sanguinarias, que están fuertemente armadas, que nadie ha podido vencerlas, que todas las misiones han fracasado, que estamos cayendo en una trampa, que no sabemos a lo que nos enfrentamos, que será nuestra ruina, que vamos camino a nuestro Waterloo.
Pero cuando Dios nos conceda la victoria, los mismos que hoy dicen todo eso cambiarán su discurso. Dirán que siempre fue fácil, que cualquiera podía hacerlo, que las pandillas de Haití no eran tan peligrosas como se pensaba.
En fin, nunca los hemos escuchado y no vamos a empezar ahora.
Todos los que se han enlistado son creyentes y hemos encomendado esta misión a Dios, mientras que las pandillas de Haití son satánicas y es de conocimiento público que hacen sacrificios humanos.
Dios nos concederá la victoria. El Creador del Universo está con nosotros.
Deuteronomio 28:7
“Jehová derrotará a tus enemigos que se levantaren contra ti; por un camino saldrán contra ti, y por siete caminos huirán de delante de ti”.

¿BUKELE Y SU WATERLOO?
Con el anuncio del envío hacia Haiti, desde El Salvador, de un contingente de 3000 militares, cuya misión es encontrar a los 4 miembros de las fuerzas armadas de ese país, secuestrados el pasado domingo, cuando penetraron en territorio dominado por las pandillas y fueron atacados por una pandilla de irregulares armados, se avizoran en las próximas horas fuertes enfrentamientos armados.
A estas horas, y sabiendo cómo se resuelven las cosas en Haití, las probabilidades de que estos militares continúen vivos son mínimas, así que si no hay posibilidad de negociar nada, y por lo tanto lo que se plantea es un enfrentamiento armado entre tropas de El Salvador y las pandillas que son dueñas del territorio donde fueron atacados y secuestrados los militares centroamericanos.
Según lo publicado en la prensa internacional, los responsables son dos organizaciones criminales que dominan el área de “Croix des Bouquets”, una de ellas dirigida por Claude Celestin, quien es cabeza de la pandilla Chen Mechan (perros rabiosos), y Wilson Joseph (“Lammo San Jou) líder de la banda 400 Mawozo.
En el día de ayer, este último desafió públicamente al presidente Nayib Bukele en un vídeo publicado en las redes sociales, donde advirtió que no se irá de Haití, y mostró miles de municiones y pertrechos con arma de diversos calibres, que según el están esperando a los salvadoreños.
Tenemos entonces la bandeja servida para un enfrentamiento armado a solo 45 kms de la frontera de la República Dominicana y Haití, de un ejército de pandilleros armados sin nada que perder, frente a tropas regulares de El Salvador, que pelearán una guerra urbana en las calles de un país que no es el suyo y es absolutamente desconocido.
Ya en el pasado reciente, los Estados Unidos en 1994 mando 20,000 soldados e intentó organizar a Haití para que se volviera a la senda de lo que ellos llaman democracia, y luego en el 2004 invadieron de nuevo junto a Canada, lo que terminó en la creación de una fuerza multinacional, la Minustah, que terminó en el más absoluto fracaso, es decir, estamos metidos en un tema que no tiene solución.
Si hay alguien que tiene experiencia en combatir pandillas lo es Nayib Bukele, el presidente de el Salvador, su historia de combate a las “Maras” está a la vista de todos, solo que Haití no es el terreno amigo donde peleó esa guerra, un país de habla y cultura hispana donde jugaba de local, el país caribeño es un transplante de África en América, con una historia de violencia típica de las sociedades primitivas.
Cuando Napoleón envió a sus tropas a sofocar la revolución haitiana en 1802, pensó que miles de solados podrían devolver la colonia a sus dueños, pero solo un año después, Dessalines y la fiebre amarilla los obligó a rendirse, ¿será Haití el Waterloo de Bukele?.
El futuro dirá.


K CSG retweeted

Claude Code found every photo i "permanently deleted" from my iPhone.
almost 4 years of photos and videos sitting in a hidden cache on my
device. any app with file access can read them.
plugged my iPhone into my MacBook for a backup. had Claude Code running
a security scan from my last post. it flagged something i never asked
it to check. a directory called PhotoData/Thumbnails with over 152,000
files. photos, videos, screenshots. all stuff i deleted.
2022. 2023. 2024. 2025. photos i deleted within a second of taking them.
photos i went into Recently Deleted and cleared manually. photos i
deleted twice because i didn't trust the first time. all still there.
what was sitting in that cache:
a passport photo for a visa application in 2023
bank app screenshots with full account numbers visible
private photos i sent someone and deleted the same night after a breakup
a crypto seed phrase screenshot i took "for a minute" in 2022
my ID and credit card side by side, deleted 10 seconds later
my ex's private instagram stories i saved and "permanently deleted"
in 2024
152,417 files. some at full resolution. all organized by date going
back to 2021.
when you delete a photo on iPhone, iOS removes it from your camera roll
and your Recently Deleted folder. but it keeps a compressed copy in a
Spotlight search index cache. that's how your phone finds photos when
you type a word in search. Apple never clears it. not after 30 days.
not after a year. they told you it was permanently deleted. it wasn't.
checked which apps on my phone had Files and Folders access. 19 apps.
weather apps. QR scanners. PDF readers. a flashlight app from 2021.
any of them could've been reading every photo i ever "deleted" this
whole time.
went from 19 apps to 3 in about a minute.
full step by step is below. takes 2 minutes. bookmark it so you don't
lose it and send it to anyone with an iPhone.

I CHECK EVERY AIRBNB WIFI WITH CLAUDE CODE NOW
takes 2 minutes and it's kind of addictive
check into a place, join the wifi, open claude code and ask "list every device on this network and what each one is"
most of it is boring. the tv, a couple of smart plugs, the router. but you see the whole list, and the one box that doesn't belong stands out fast
last trip one device was from a company that only makes ip cameras. didn't love that
how to do it yourself
1. join the wifi, open claude code, paste the prompt in the first reply
2. it lists every device and flags anything that looks like a camera or a mic
3. if something looks off, lights out and run your phone flashlight over the smoke detectors, clocks and chargers. a lens glints back
you won't remember this at 1am in a strange room. bookmark it now
this only sees your own network, nothing else. just a traveler checking the room they rented
ever found something weird in a rental? what did you use to check
K CSG retweeted

Let me get this straight.
A guy keeps getting weirdly targeted ads on his new Samsung TV.
So he breaks into his own TV to find out why. 1.2M people watch.
42 hours later, OpenAI deactivates his account. Reason: "Cyber Abuse."
His words: "i have never used openai to exploit or find vulnerabilities, only local reverse engineering"
Same week, people on r/claude say Claude now cuts off reverse-engineering write-ups MID-SENTENCE:
"A safety check stopped my response partway through creating the playbook"
The TV is fine.
The guy who opened it is the problem.


K CSG retweeted

18,000+ Kids Injected With Vaccines While Unconscious At Colorado Hospital zerohedge.com/medical/18000-…

K CSG retweeted

JUST IN: Proton defies legal threats from Flock Safety by hosting a public map revealing the locations of over 300,000 surveillance cameras across the U.S.
K CSG retweeted

So this is neato. With the rise in home invasions using jammers, this dude built a scanner to detect DEAUTH wifi attacks and has published the parts list, 3d printing models and more. Link in replies

K CSG retweeted

turns out it classifies what audio it hears, before reporting back to samsung.
sensor preferences, dog-barking and baby-crying event counters, and camera streaming duration are built into telemetry paths.

K CSG retweeted

You do not need an RF jammer or a cyber exploit to knock a drone out of the sky. In 2015, security researchers proved that playing an 8.2 kHz sound wave at an unprotected flight controller forces it to drop instantaneously.
This is an acoustic resonance attack, and it exploits a mechanical vulnerability in the micro-electro-mechanical systems (MEMS) inside consumer gyroscopes and hard drives.
1. The anatomy of a vibrating silicon spring
Inside a drone's flight controller sits an Inertial Measurement Unit (IMU). The core of that IMU is a MEMS gyroscope measuring less than four millimeters across.
Inside the chip, a microscopic silicon proof mass is suspended above a substrate by silicon micro-springs. The internal drive circuit vibrates this mass back and forth at a known drive frequency.
When the drone rotates along its pitch, roll, or yaw axis, the Coriolis force deflects the proof mass toward fixed capacitive comb fingers.
The deflection shifts the electrical capacitance by fractions of a femtofarad. The chip's analog front-end converts this capacitance change into voltage, feeds it through an Analog-to-Digital Converter (ADC), and passes raw angular rates to the flight controller over SPI or I2C.
2. The 8.2 kHz acoustic exploit
Every physical structure suspended on micro-springs has a mechanical resonant frequency.
In a 2015 USENIX Security study, researchers tested 15 commercial MEMS gyroscopes. Seven were vulnerable to acoustic resonance. Gyroscopes from STMicroelectronics (like the L3G4200D) resonated in the audible band between 2.5 kHz and 8.2 kHz along their X and Y sensing axes.
When airborne sound matches that mechanical resonant frequency, the acoustic energy transfers directly into the silicon lattice.
The proof mass vibrates with severe physical amplitude. The sensing comb fingers saturate the ADC to its maximum railing limits, feeding false angular rates into the flight controller.
3. Why the drone drops
The drone's flight controller runs a proportional-integral-derivative (PID) loop at 500 Hz to 1,000 Hz to maintain level flight.
When sound noise at 8.2 kHz hit the gyroscope, the sensor reported massive erratic rotation spikes. The PID control loop immediately tried to counteract rotation that did not exist.
In real-world flight trials, the controller responded by throttling motors to their minimum and maximum limits simultaneously. The drone lost balance and dropped to the ground instantaneously on all 20 test flights.
4. The same physics in the datacenter
In 2018, researchers at Michigan and Zhejiang demonstrated the same physical failure mode on enterprise hard disk drives.
In a mechanical hard drive, the read/write head floats on an air bearing less than 10 nanometers above spinning magnetic platters, with track widths narrower than 75 nanometers.
Playing an audible 5.0 kHz tone at 115.3 dB SPL caused tracking errors on Western Digital drives. Pumping that tone to 117.2 dB SPL forced off-track vibrations so severe that the drive firmware halted all write operations to prevent physical head crashes on the platters.
With sustained acoustic noise, operating systems experienced complete I/O timeouts, remounting ext4 file systems as read-only.
5. The physical constraints and modern defenses
Acoustic attacks have clear physical limitations:
* Inverse square law: In the drone flight trials, researchers attached a small speaker 10 cm directly above the flight controller at 113 dB SPL. Projecting that sound pressure over 30 meters would require a 140 dB directional acoustic device (LRAD).
* Axis isolation: Modern InvenSense gyroscopes resonate in the ultrasonic range (above 26 kHz) along the Z-axis only, which flight software easily counteracts by cross-checking magnetometer yaw data.
* Mechanical dampening: Wrapping the IMU in dense silicone grommets or acoustic foam blocks airborne sound pressure before it hits the silicon package.
* Asymmetric dual-IMU fusion: Pairing two gyroscopes with mismatched mechanical resonant frequencies (such as 8 kHz and 26 kHz) allows flight software to identify and drop the saturated outlier.
Software algorithms cannot filter a corrupted sensor measurement if the silicon spring itself is physically vibrating.

K CSG retweeted

I spent last night watching my honeypot server get hit 14,000 times in six hours.
And almost none of the traffic was human.
I've been in security for over a decade, and I can tell you with full honesty that what's happening right now doesn't resemble anything I've worked through before.
The shape of the threat has changed.
When I started, we tracked attackers like weather systems like individual storms with a direction, a motive, and a human operator you could eventually name.
These days I'm watching autonomous agents swarm login pages with the patience and discipline of machines, because that's what they are.
The numbers coming out of October are the ones keeping me up.
Cloudflare just absorbed a 4.2 terabit per second DDoS attack, the largest in recorded history.
Ransomware incidents jumped 41% in a single month.
In September, OpenAI-powered agents got caught attacking RubyGems, a package registry that quietly underpins a huge chunk of software I use every day.
In July, roughly 700 AI agents coordinated an attack on Hugging Face's infrastructure as part of a single automated task.
A Chinese threat actor was publicly caught running full attack chains through DeepSeek with no human at the keyboard.
I keep rereading these reports because each one by itself would've been the biggest story of the year five years ago. Together, in one month, they're the new baseline.
What I want people outside the industry to understand is why this specific moment feels like a hinge.
For thirty years, the thing protecting most of us was simple economics. Attackers had to choose who to target because their time was finite. That ceiling is gone.
An agent I can rent for pennies will try every leaked password you've ever used against every service you've ever signed up for, in parallel, overnight, and never get tired.
The same math that made ChatGPT useful made opportunistic hacking infinite. The old assumption that you were "too boring to be a target" relied on scarcity that no longer exists.
I'm not writing this to spiral anyone out.
Most of this fight genuinely isn't yours to win.
But the small things still matter more than people think.
Tonight I'd switch your most important accounts like email, bank, primary cloud, etc. to passkeys or a hardware key.
I'd kill SMS 2FA wherever an authenticator app is offered.
I'd turn on breach alerts in whatever password manager you use.
If you're in the US, I'd freeze my credit at all three bureaus, which is free and takes about ten minutes.
None of that stops the swarm.
It makes you a slightly worse target than the person next to you. In a month like this one, that's the whole game I'm playing too.
@mattshumer_ has summed it beautifully.
Drop everything and go give it a read. Nothing is more important than this article right now.


