

Technologist - Investor - Motorcyclist - Armchair comedian - Soothsayer - Instigator - Armpit scratcher - Professional bum - 🇲🇾
Alphaque. Anytime. Anywhere.
Joined March 2009
- Tweets16.8K
- Following2K
- Followers3.4K
- Likes7.1K






Dinesh Nair retweeted

RSAF operates ~40 F-15SG and ~59 F-16s. Training detachments keep up to ~12 F-15SGs in Idaho and a smaller number of F-16s in Arizona, so the large majority remain based in Singapore at Tengah and Paya Lebar. No F-35s are in Singapore yet (first deliveries go to the US late 2026; 8 F-35As planned for Tengah from 2029).

Dinesh Nair retweeted

🇲🇾 🚨 RHYSIDA RANSOMWARE CLAIMS ATTACK ON MALAYSIA'S INTI INTERNATIONAL UNIVERSITY & COLLEGES
The Rhysida ransomware gang has listed INTI International University & Colleges, one of Malaysia's largest private higher-education groups, as a new victim on its data-leak site.
The listing, dated Oct 30, 2026, does not say what data was allegedly taken or how much, and no samples have been verified.
The claim has not been independently verified, and INTI has not publicly confirmed an incident.
⚠️ Analyst Note:
Rhysida has a long record of hitting universities and schools, and in past cases it auctioned stolen staff and student records, including ID documents. CISA and the FBI have warned that the group uses phishing and Cobalt Strike to get in and runs double extortion. INTI students and staff should watch for phishing that uses university branding. Treat this as an UNVERIFIED threat-actor claim, NOT confirmation of a breach.
#DDW #DarkWeb #Ransomware #Rhysida #Malaysia #HigherEducation #INTI #DataBreach #ThreatIntelligence #CyberSecurity

Dinesh Nair retweeted

First tampered Ledgers, now a reported implant in a Trezor Safe 5. Same reseller, CryptoBilis. Trezor has gone public fast, with help from @SEAL_911. Whoever is behind it, that shop is compromised. If you bought there since March, get a new seed.

CryptoBilis update
We've been made aware, through responsible disclosure, of a single hardware implant in a Trezor Safe 5 device bought from the reseller CryptoBilis in August 2026.
No CryptoBilis buyer has reported a loss of funds to us.
IMPORTANT: If you bought a Trezor from CryptoBilis from March 2026 onwards, we know this is unsettling. Here’s what to do:
Already using it?
Move your funds to a newly created wallet with a new seed as soon as possible. Do not reuse the old seed in any wallet, hardware or software. If you don’t have another secure hardware wallet available, we recommend temporarily migrating your funds to a software wallet or an exchange you are familiar with.
Not set up yet? Don’t set it up, and never enter your existing wallet backup on it.
We haven’t received the device to confirm this report, but based on the customer’s description, we’re treating it as credible and sharing it now so customers who purchased a Trezor via CryptoBilis can secure their funds as a precaution. Our security team will examine the device as soon as it arrives.
On October 9, 2026, we removed CryptoBilis as a reseller following reports of tampered Ledger devices sold through it. Since then, we have been inspecting Trezor devices that customers bought from CryptoBilis and have found no signs of tampering on any of the four devices we’ve received so far.
NEVER share your wallet backup (recovery phrase) with anyone. Trezor Support will never ask for it.
If you are affected by this incident, please keep your CryptoBilis device and contact Support to receive a new Trezor hardware wallet: trezor.io/support#open-chat
We're investigating and will post updates here as soon as we know more. Thank you to the customer who reported this through our responsible disclosure program, and to @SEAL_911 for working alongside our teams on the response. Reports and engagement like this help us protect everyone else.
For more information, visit our blog: trezor.io/blog/news/implant-…



Dinesh Nair retweeted

This is why it's called "decentralized finance". One minute it's your money in your wallet and the next minute it's decentralized in hundreds and thousands of anonymous wallets. 😂

Dinesh Nair retweeted

pbxscience.com/freebsd-co-fo…
FreeBSD Co-Founder Ports Omarchy to FreeBSD in Ten Days, Ships Ten Releases.
One of the original founders of the FreeBSD project, has released Daemonarchy, an installable #FreeBSD image that brings the look and workflow of the Omarchy desktop to #BSD....


Dinesh Nair retweeted
Ok cuba try, what has Malaysia produced with this compute super powers?
Do we have apps which are conquering the world? What about some groundbreaking math discovery? Maybe a promising startup everyone is talking about?
Are there high income jobs created, or did we sell our energy and water cheaply so someone can boast?
Dinesh Nair retweeted

Vibe coder: I made a terminal and it's faster than everyone!!!
Legendary engineer:

I like to look at claims like this in case I can improve Ghostty. I grabbed your source and immediately spotted the issue: your read loop overwrites a 64 KiB ring. Everything older is discarded unparsed per tick. You're faster because you're not actually terminal emulating.
It means the number isn't a throughput number. In a kitten benchmark run at the rate you're claiming, roughly 6.6 MB arrives per 60 Hz tick and 64 KiB of it gets parsed. You're read(2)-ing 100% of the data and parsing about 1% of it.
There are other minor issues (a small fixed scrollback in a preallocated ring buffer, no grapheme clustering, throwing away data like OSC 8 URIs, etc.), but the major one is simply that you're discarding ~99% of the input.
For plain text, e.g. your cat benchmark, the final screen ends up looking right, but the scrollback is missing 99% of the file and each retained chunk starts mid-line. As soon as there are escape sequences in the dropped spans, your emulator is fully out of sync and invalid: a cut inside a CSI prints the parameters as text, and any SGR, mode, title, or alt-screen change in the gap is just... gone.
FYI, this is why I don't like when people point at refterm as a terminal benchmark. refterm implements a TINY subset of what a terminal emulator must support, it's closer to a fast file reader, not a terminal emulator.
I also don't mean any shade by this. I like to look at technology objectively to try to learn something and improve my own craft and work. So I'm sharing what I found.
I modified your code very slightly to parse on every full buffer (rather than per tick). And the results are attached. Both use main commit in each repo at the time of this post.
Note the graph is in log scale, the discrepancy between performance for things like Kitty images is measured in GB/s.


Dinesh Nair retweeted

🚨🗣️ Ian Wright: When it’s Arsenal, the refereeing is always different!
“How on earth was that a red card? Seriously, what are we doing here? The Fleetwood player tackles Max Dowman, Max barely reacts, and the referee immediately reaches for a red card. Unbelievable!
We saw a similar incident last weekend in Chelsea vs Tottenham, when Cole Palmer reacted after a challenge, yet the referee didn’t send him off. So why is the standard suddenly different when it comes to Arsenal?
I’m not saying Arsenal lost because of that decision, but it undoubtedly affected the game. That was never a red card in a million years!
Sometimes, I genuinely feel Arsenal are officiated differently. If you’ve watched that incident and still believe Max Dowman deserved a straight red, then honestly, football is not for you.
Young players deserve protection, and Arsenal deserve the same standard of refereeing as everyone else. Enough of these inconsistent decisions!
#FLEARS


Dinesh Nair retweeted

Announcing 3 Critical vulns for hundreds of millions of IoT, Firewalls, OT, and Military devices including: Palo Alto Networks, Comcast, D-Link, HP, Canon, Honeywell, GE, Oracle, Siemens, Rockwell, Digi, Lockheed Martin, Boeing...
The vulns are with GoAhead Web Server which is a backend library used by these devices. There's a patch available from GoAhead but that doesn't mean there's a patch available for the devices yet -- that's up to the manufacturer.
- TLS traffic over DHE ciphers have a 1-byte secret, "04", meaning anyone can decrypt connections to these devices and steal login credentials and session tokens if the client negotiated with DHE ciphers like the latest TLS_DHE_RSA_WITH_CHACHA20_POLY1305_SHA256, which is extremely likely.
- LibreSSL mTLS has been completely bypassed, meaning anyone can connect over mTLS. If you have one of these devices listening on the internet and are expecting mTLS to protect it from attackers, take it offline or patch asap.
- OpenSSL Certificate Revocation Lists (CRLs) are not enforced, meaning if a user device is stolen or compromised, and you revoke that mTLS cert, nothing actually happens. There are a lot of other attacks this can be used for.
These are critical because these types of devices run our world. Water systems, electricity, military, firewalls, critical infrastructure.
foxio.io/blog/choose-your-ba…

Dinesh Nair retweeted
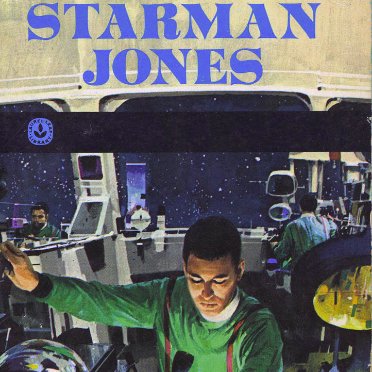
Behold: The US Defense Intelligence Agency has released a report on challenges to security in space, including an NEI image of China’s spaceplane from Maxar, taken in 2024.

Dinesh Nair retweeted

Daemonarchy is bringing Omarchy's Wayland-based desktop to the BSD world.... More here: theregister.com/os-platforms…


Dinesh Nair retweeted

“who should we lay off first”
CEOs:

BREAKING: Microsoft, $MSFT, is offering buyouts to 60,000 workers as part of the company’s efforts to cut costs amid AI adoption, per Bloomberg.
Personnel on select teams in the US, Canada, India, and the UK at a vice president level and below will be eligible.
This reflects ~27% of Microsoft's total workforce.
Dinesh Nair retweeted

Daemonarchy keeps Omarchy’s installer and look, with FreeBSD handling the system underneath.
itsfoss.com/news/daemonarchy…
