

I build tiny start-ups and test SaaS + AI tools so you don't have to 🌅 Honest reviews, real numbers, tips that work.
Australia
Joined October 2026
- Tweets182
- Following101
- Followers108
- Likes540




Can’t wait to download and not be able to use the latest models 🙏🏻🤣

Best thing I've seen on the internet today
antigravity.google.com

Bro took 2 users and said “SAAS is officially dead” 🤣

SaaS is officially dead 🥀
Marc's Datafast has lost $2k in MRR and ~50 subs were cancelled in last 30 days. It's falling at a rate of ~$60/day.
> It’s just a script tag and a dashboard. Switching takes 10 minutes.
> No real data lock-in. Export, paste a new tag, done.
> It has no real MOAT which prevents people from copying it.
So the only thing keeping customers is inertia. And inertia expires the moment someone does the real math.
I made databull.app, a one-time, self-hosted version of datafast. Many of my customers are ex-datafast users who cancelled their subs to reduce their monthly expenses or wanted to own their data.
Customers who don't see value in paying for subscriptions will eventually switch no matter how big your audience is.
So focus on the MOAT from day one because it is the only thing in this era which can save your SaaS from dying.
And honestly speaking, TrustMRR was a genius move by Marc. It's the perfect example of a SaaS which can never die.


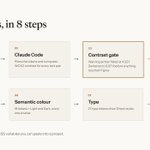
Paste this into Claude Code and run it daily:
Build me a daily security check skill. Step 1: read Cloudflare Zero Wire (radar.cloudflare.com/securit…) and triage every CVE against my actual stack, not in general.
Step 2: inventory everything that runs code on this machine and any server I can SSH into: OS and kernel, runtimes (Node, Python, PHP, Go, Java, Ruby), package managers, Docker images, browsers, browser caches used by Playwright or Puppeteer, Electron apps, CLIs, npm/pip/cargo audit.
Step 3: compare each against the latest release and end-of-life dates.
Step 4: tell me what is behind, what is EOL with no fix coming, and what to run to fix it. Never change anything without asking.


solid security prompt: Ran with Fable 5.1 and deployed 2 agents on Opus 5.5.
"Find every place my app trusts the browser too much"
Found 7 high risk bugs in my app.


