





Pivoting on the proxy providers observed here and the device, we narrowed it down to a single likely app. With high confidence we believe this to be the app providing network access into the Whitehouse.


This has been several months of research, digging through complex backdoors and exploring an otherwise undocumented space. Happy to see the research finally public 😄 Congrats to all of the teams involved 🎉
Residential proxies, ad fraud, and credential theft have flourished through sophisticated pre-infected device schemes. This research, in partnership with the @motionpictures and in collaboration with @Google, @trendaisecurity , @BlackLotusLabs , and @SecureWithHUMAN, disrupts one of these operators.
Synthient’s Research Team documents its findings in this report, showing how the operators distributed over 1.3 million devices to unsuspecting consumers and how this supply chain pushed numerous backdoors from APSolo to Honeygain.
Read more here: synthient.com/blog/the-inter…

Indicators of compromise and observables as always can be found below:
github.com/synthient/public-…


Flux Proxy SDK being dropped as part of ongoing compromise global[.]proxystream[.]st


Surreal to see some of the @synthient research mentioned by @AnthropicAI :) Super cool
anthropic.com/research/self-…

One of my friends found this pretty bug that allows you to impersonate Grok bot. Reported but never heard back.
nightd.dev/blog/impersonatin…

The IPWeb operators have purged everything from GitHub post-publication. Guess they aren’t a fan of #opensource 😔


> be chinese financially motivated threat actor
> create big ass fuck off botnet
> botnet transforms machines into proxies
> sell proxies on IPweb
> make big money
> millions of dollars
> accidentally push source code of botnet to GitHub
> accidentally push source code of botnet to GitHub
> @synthient finds it
> hello mr synthient can i have the goop code?
> "sure?"
> gives
> download it
thank you mysterious group of chinese people for accidentally uploading your botnet code to github. i have goop code now


Chinese-speaking proxy services are often grouped together as belonging to IPIDEA or Kookeey. In reality, the ecosystem is incredibly diverse and includes a number of custom botnets. This report focuses on one of those providers: IPWeb.
In our latest research, we reveal the inner workings of APSolo, one of the largest Chinese proxy botnets. The botnet continues to fuel DDoS attacks, fraud, and other cybercrime. Using multiple source-code and infrastructure pivots, we linked it to the Chinese proxy provider IPWeb.
Provider: IPWeb
Malware Family: Proxyware.APSolo
Size: 800K - 1.2 million daily active IPs
Full Story: synthient.com/blog/ipweb-pee…


Ben retweeted

Two Australian TeamPCP members were arrested today.
Here's the arrest footage:
Arrest of 23 year old in Mandurah.
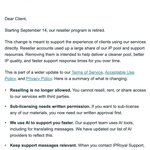
IPRoyal planning to terminate their reseller program starting September 14th. This likely comes following the NetNut disruption. Will be interesting to see if this includes their own reseller brands such as Marsproxies.

Orbit is highly active with a large portion of attacks targeting #discord along with small websites. Interestingly there is another C2
coxm[.]duckdns[.]org responsible for delegating attacks.


#Sysorbit is an Android DDoS botnet disguised as "Google Play Service." It is derived from the Mirai family but has been thoroughly adapted for the Android environment.
apk hash: 6b926acb42e6519747d72ddb0bfecb8f4e346d28
cnc: tblcxmo.duckdns[.org udpatetbl.duckdns[.org