




Kapeka retweeted

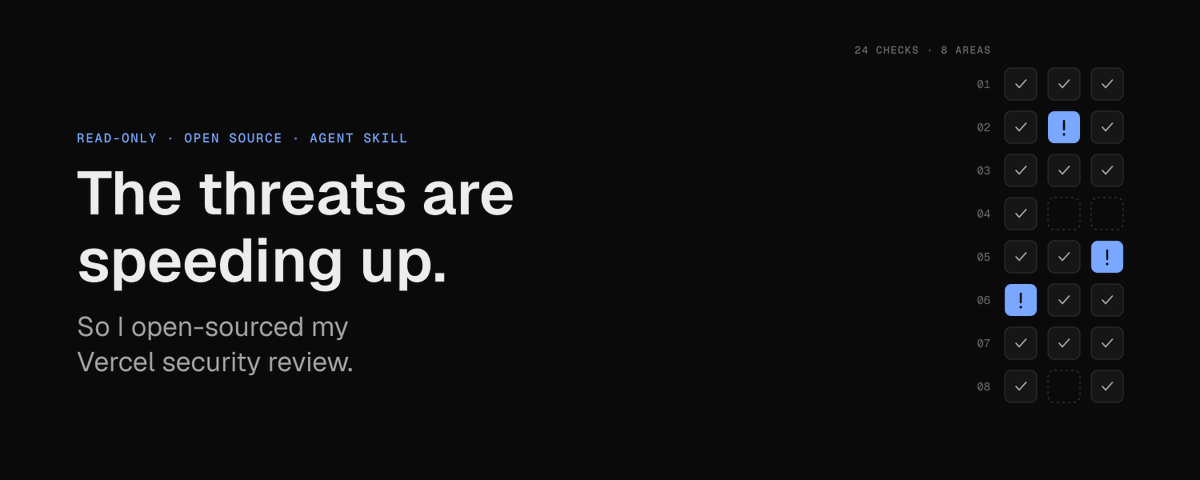
Today we are launching Vercel Security Review in public beta.
Run vulnerability reviews on every push, and ship fixes in one click with Vercel Agent.
Read the blog → vercel.com/blog/vercel-secur…

Kapeka retweeted

Day 28/ tibo's game has landed
i spent $5.99 on this domain, but i had a blast making it with grok bot and cursor! i hope you enjoy it and find all the easter eggs 🤍
if i did it right you should be able to play it inside of X too
tibo.dog

Kapeka retweeted

Introducing agent-desktop
agent-browser, for your whole computer
→ Computer Use for any coding agent
→ macOS, Windows and Linux
→ Runs in bg while you keep working
→ Agents use your computer in parallel, each with its own cursor
Kapeka retweeted
Introducing Vercel CI
• Intelligently skips tasks with Turborepo
• 2-6× faster CI in our internal repositories
• Optimized for agents via Vercel MCP and CLI
After nearly 8 million tasks, we're excited for the future of agentic CI. In beta on all plans.
vercel.com/blog/introducing-…

Kapeka retweeted

To teach a lesson,
After Wiz rushed to buy php2shell domain and use its marketing machine to steal the spotlight, I spotted "phpbleed" in a recent Calif tweet and bought phpbleed.com before wiz could pull the same stunt again.
A big budget can buy a domain. It shouldn't buy someone else's research credit.
If you have contacts at CISA or in the press, do the right thing: make sure the researchers who actually did the work get the recognition they deserve.
Hack the planet. Credit the researchers.


So tired of guardrails,
Open AI made us buy hardware keys to then eliminate cyber capabilities of every model
Cancelling my Open AI & Anthropic Max plans to buy more Deepseek credits
The future of frontier cyber models are open weights models

We found DeepSeek V4.1 Flash 1017 beats GPT 6 Sol on our multi-step offensive cybersecurity task. Sol was tested via the Daybreak trusted access program.
We have been building a cybersecurity benchmark based on simulated corporate networks. This is a valuable indicator for the cyber-risk a model poses if in the hands of a bad actor. We plan to make the full evaluation public in the coming weeks but wanted to share our first immediate finding here.


- Anthropic/Open AI models with TAC + Yubikey:
This content can’t be shown
- Deepseek V4.1 with free tier:
Reverse-engineered a V8 n-day
→ V8 arbitrary R/W
→ Main World escape via JSGlobalObject
→ Abuses bundler module loader
→ Privileged Electron IPC
→ OS RCE
299

Kapeka retweeted

The details of the long awaited KVM Escape are published. PwnEscape leads to VM escapes across multiple hypervisors due to a super cool Linux networking bug.
CVE-2026-99999 is a 9.3 CVSS critical rated KVM escape ⛓️
pwn.ai/blog/pwnescape

Kapeka retweeted

Introducing PwnEscape 🦉: a full KVM guest-to-host escape via a Linux kernel networking flaw affecting industry standard hypervisors.
CVE-2026-99999 went from untrusted VM code to host-kernel memory reads, controlled writes, and root command execution. More below:
🤖 Made with AI

Kapeka retweeted

You’re right, @Jason!
This is a golden age for white hats.
The bounties are real. Companies pay for confirmed bugs from whoever finds them first.
What we're lacking is enough skilled hackers to check all the code being written.
The way we see the market going is white hats directing teams of AI agents.
Just like we did here ↓
xbow.com/blog/xbow-built-a-c…


I don’t understand hackers that still say that it’s the end for bb
like, the game is changing, for sure, but software by design will have bugs
and internal pipelines will not be able to catch all of them
i think bb will be more fun because bugs will require more deep system thinking
2
314
Kapeka retweeted
This idea could geniuley transform bug bounty and really align incentives of most researchers and hackers, as well as help the internet find the nastiest bugs really quickly. This is a top tier CTO comment and if done, I have no doubt it would start a security revolution! So many talented hackers don't even look bc reporting etc is just a mess, or often just unrecognized so god knows what's buried in random dependacies of the everyday tools we use. 1000% agree

Funnily enough, I broadly agree with Mr. @DeGatchi. For vulnerabilities like this one which impacts everybody using KVM (read every hyperscaler, every AI lab, every company on the planet really), there should be a fund that pays from all of them.
As Vercel we are trying to do our part here. And all credit to @PaulosYibelo for going down the pass of responsible disclosure!
