

https://xitter.cf/t.co/91H5qeHXaJ - I write about the practical side of AI. Latest: what context (doesn't) transfer between tools, and the standards & OSS fixing it
Seattle, WA
Joined December 2008
- Tweets1.7K
- Following604
- Followers435
- Likes596

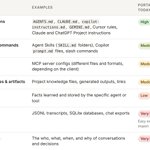


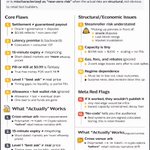


Cuban and Tracey are arguing about AI memory portability. They're both right, about different layers. Portable today: instructions, skills, MCP configs. Stuck: memory, chat history, metadata. Details: peckjon.substack.com/p/ai-po…


Right or Wrong ?
Switching costs for consumer AI, won't approach zero until there is a standardized export format for what is in a model's memory.
The more a consumer uses a model, the more it's memory stores. The more work to export and import
I'm not saying it can't be done. Obviously you can import from one model to another. But for regular users, that's a lot more difficult than saving to an xls or doc file
Curious what people think ?

Jon Peck retweeted

AI is reshaping DevOps – but how do you scale smarter, faster, and more responsibly?
At ODSC AI West, @peckjon, @github, will share real-world strategies in his talk:
Scaling AI-Driven DevOps: Smarter, Faster, and More Responsible Workflows.
Register → hubs.li/Q03Q034q0

Help us out @daftpunk, our codebase is never over suno.com/s/sSl45Qiqe2bHUAZQ


Jon Peck retweeted
We’re thrilled to welcome @peckjon (@GitHub) to ODSC West 2025! 💻
If you’re building AI-powered developer workflows, or want to see what’s next for AI + DevOps at scale, Jon’s insights will be invaluable.
Don’t miss out! Register now -> hubs.li/Q03CNZ9B0

Hey @ThousandTrails did you take a page from the Timeshare sales sleazebook? Call your “infosessions” what they are: thinly-veiled high-pressure upsells.
Customer loyalty grows from trust & transparency. Deceit only begets churn.
Took a day, built a thing — for fun, not to sell. But possibly interesting to anyone building data pipelines or just looking for a vibe code -> iterate -> demo app example. Blogpost & repo: peckjon.github.io/daft-image…
A few years ago I was deep in the trenches at Algorithmia, wrestling Jupyter notebooks, memory bugs, and gnarly data pipelines.
Today? I built an AI image search engine in hours using @github Copilot + Daft.ai
The future’s here.
👉 peckjon.github.io/daft-image…

Data pipelines used to be a mess of custom scripts and orchestration hell. But AI pair programming and a tight data tool (Daft.ai = multimodal at scale + nonrelational SQL) accelerate everything - if you know how to guide it them! Blogpost & repo ^^
Jon Peck retweeted

GitHub's @peckjon & @ladykerr built the same app 3x using GitHub Copilot: GPT-4, Claude 3.5, & Gemini 2.5
What they learned:
– Prompt > model size
– Agent mode is 🔥 but needs oversight
– Custom instructions = underrated
Full demo: github.blog/ai-and-ml/real%e… #GitHubCopilot #AI

ALT Real‑world video demo: Using different AI models in GitHub Copilot
UI is super-primitive right now, but I wanted to share creativecradle.com for all those trying to find domain names that aren’t already squatted/auction. Describe your idea, AI finds and ranks available domains. Feedback welcomed.

CORS: I’m a helpful protocol for ensuring requests come from the right source!
Me: and you’re easy to set up?
CORS: not really
Me: with great support for local dev?
CORS: also no
Me: but at least you’re hard to circumvent and help prevent real-world attacks?
CORS: so about that…
Come work with me at @github #DevRel! While much of our work is remote, you’ll need to be within commuting distance of Munich for this one: githubinc.jibeapply.com/jobs…
Looking forward to trying you out @achromaticlabs — your docs were the hook. Straightforward and well-written with great examples. I can tell that using your framework will be a pleasure.
Jon Peck retweeted

We got to see 5 incredible devtools demo AI live at Dark Mode ⚡️
The end of README, an AI app built in 5 minutes + more!
Now ready for you to watch 🍿 jam.dev/blog/ai-demos-from-d…

Jon Peck retweeted

Please share this far and wide. As far and wide as you can. NIST Password Guidelines for 2024 are in the process of being updated.
This is a HUGE pet-peeve of mine (when vendors in particular are still operating like its 2017 and keep changing passwords every 60 days, STOP DOING THIS, it's outdated and has been shown to put you MORE at risk than less -- NIST explains why it does in this document, meticulously outlining user behavior**) so I'm sharing this in the hopes all of you will pass it along to your bosses.
The Special Publication series governing passwords is SP 800-63 "Digital Identity Guidelines".
The 2024 version is 800-63-4.
Here: pages.nist.gov/800-63-4/
The companion docs are also on that link. They are 800-63A, 800-63B and 800-63C. These are different documents for different scenarios in play at your org.
The previous update was in2020.
The changes in the 2020 version from the 2017 version were numerous but one of them was that the password verification method should NO LONGER require passwords be changed at specific intervals (i.e. every 60 days) but in the following circumstances instead:
1. After a breach/compromise
2. User request
2024 repeats this and adds a bunch more guidlines but here is a screenshot of page 13 of the new 800-63-4 (note the # 4 after it) which outlines how your systems should now and moving forward, be handling passwords.
This goes for Active Directory, too. All your systems which have passwords should align with these guidelines provided there isn't another standard or framework you must adhere to which overrules this.
Most frameworks, however, have moved away from arbitrary password resets and complexity rules.
**We cybersec researchers and hackers use wordlists from breaches in a variety of different ways. Hackers use them in tooling to crack passwords whereas researchers use breach dumps to see the kinds of passwords users are creating and the psychology behind them.
Using complexity rules gets you the user psychology of:
Password1
Password2
and so on
Use phrasing instead and allow for spaces, which is important. Humans type phrases with spaces. They also mention phish-resistant methods and most vendors are on-board with MS going to be turning off all Legacy Auth next month, across all free accounts and tenancies.
I'm so excited for the new changes!
Ok I'm off my soapbox.
Share the love! Thank you!
