





Cesar Chavez Martinez retweeted

A developer left a PHP server vulnerable to the new PHP2Shell flaws and put a Bitcoin key on it, challenging hackers to steal the funds.
After around 19 hours, a researcher known as KillaBoi successfully exploited the vulnerability and extracted the private key.
The wallet contained around $2,000, but the key turned out to be linked to the wrong wallet, so the funds couldn’t actually be taken.
The dev still confirmed the exploit worked and paid the researcher the prize.


Cesar Chavez Martinez retweeted

UPDATE: UNIT 42 RETRACTS PHP2SHELL EXPLOITATION UPDATE
Unit 42 has retracted its Oct 23 update that tied a European government intrusion to PHP2Shell (CVE-2026-109618 / CVE-2026-109619). It says it is unable to confirm that initial access was associated with those CVEs.
The CVEs remain critical unauthenticated RCE (CVSS 9.2). Patching guidance and the ~22.6M exposed-instance figure still stand. Our Oct 24 “UNIT 42 CONFIRMS…” post is superseded by this correction.
unit42.paloaltonetworks.com/…
#DDW #PHP2Shell #Unit42 #CyberSecurity #ThreatIntelligence

Cesar Chavez Martinez retweeted

❗️ A bug in Microsoft Authenticator let an Android app with zero permissions pose as Teams and steal a user's work-account tokens.
In Enclave's tests, the tokens opened the victim's mailbox, files and calendar with no prompt.
Microsoft fixed it in July as CVE-2026-80097.


Cesar Chavez Martinez retweeted

Hay un tendal de personas que han perdido acceso a su WhatsApp. No es un "hackeo", mucho menos una "clonación", hasta hoy hallé 3 vectores:
1) SIM Swapping o transferencia fraudulenta de titularidad del chip de la víctima al victimario. Hablar con la telefónica, denuncia policial
Cesar Chavez Martinez retweeted
面白いサイトが現れた。
例のPHPの脆弱性「php2shell」、実際に完全なRCEまで辿り着いて悪用している例が少なすぎて「わざと脆弱なまま放置したよ!自由に乗っ取ってね、30万円分のBitcoinウォレットも置いときます」という挑発サイトが爆誕
stealmybitcoin.com/

Cesar Chavez Martinez retweeted
WATCH: Migrant Uber Eats delivery workers in France are using multiple phones to reject low-paying orders, forcing the app’s algorithm to raise delivery offers to €15 or more.


Cesar Chavez Martinez retweeted

Security Alert: U.S. Mission Saudi Arabia (October 25, 2026)
Effective October 23, 2026, the Department of State ordered non-emergency U.S. government employees and U.S. government employee family members to leave Saudi Arabia due to safety risks.
Iranian-supported Houthis have engaged in hostilities against Saudi Arabia, including attacks on civilian airports and other critical infrastructure resulting in civilian casualties and severe travel disruptions. The hostilities have the potential to escalate rapidly beyond that immediate area.
U.S. government employees working in Saudi Arabia require special authorization from Chief of Mission to use any airport in Saudi Arabia following recent missile and UAV attacks on airports in the Kingdom.
King Khalid International Airport (RUH) in Riyadh announced a partial reopening as of October 25 for domestic flights and some international flights operated by national carriers. A limited number of flights normally based at RUH are operating out of Qassim-based Prince Naif bin Abdulaziz International Airport (ELQ).
Operations at King Abdulaziz International Airport in Jeddah (JED) are operational with some delays and cancellations.
Operations at King Fahd International Airport in Dammam (DMM) are operational with some delays and cancellations.
U.S. citizens should be aware of potential attacks on airports, airspace closures, flight cancellations, and travel disruptions. Please take extreme caution if you choose to use airports in Saudi Arabia. We recommend checking your flight departure status directly with the airline and with the airport.
Read more: sa.usembassy.gov/security-al…

Cesar Chavez Martinez retweeted

Someone has created a vulnerable PHP website, loaded it with a Bitcoin wallet, and challenged the Internet to hack into it and they can keep the Bitcoin. It has a running timer to show if the PHP exploitability was over-hyped. stealmybitcoin.com/
Cesar Chavez Martinez retweeted

Php2shell-scanner Tool for scanning php2shell using 3 methods: via URL, localhost, SSH
github.com/aancw/php2shel


Cesar Chavez Martinez retweeted

Everything that's made on gob.pe is run by an obseletr php. Most SSL won't load on any other explorer that isn't edge since it's the only one that's still accepts them.
Cesar Chavez Martinez retweeted
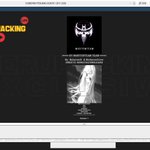
🇨🇳 🚨 HISENSE NAMED BY "WHITEARMOR" EXTORTION GROUP
WhiteArmor, the new data-extortion group behind the Whirlpool and J.B. Hunt claims, has listed Hisense, the Chinese electronics and home appliance giant, on its leak site.
The listing reportedly claims:
* A warranty-claims archive tied to Hisense operations in Malaysia and Singapore
* Customer IDs linked to those claims
* Records on roughly 2,500 suppliers
The group is reportedly asking $500,000 and has set a late-November release deadline.
The claim has not been independently verified, and Hisense has not publicly confirmed a cyber incident.
⚠️ Analyst Note:
WhiteArmor surfaced on Oct 21 and has moved quickly through large consumer brands. The claimed scope points to a regional service or warranty system rather than a company-wide breach, and actor-stated figures may be inflated or recycled. Customers in Malaysia and Singapore should watch for warranty or service-themed phishing. Unverified threat-actor claim, NOT confirmation of a breach.
#DDW #DarkWeb #WhiteArmor #Hisense #Electronics #Extortion #DataLeak #ThreatIntelligence #CyberSecurity

Cesar Chavez Martinez retweeted

Update to #PHP2Shell Alert: SIGMA rule helps identify potentially suspicious activity & incorporated partner resources. If your org can't update immediately or uses unsupported PHP 8.1 or earlier versions, take affected PHP-based systems offline until patched or updated.

🚨 Organizations should immediately patch critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. These vulnerabilities enable unauthenticated #RCE and affect PHP installations serving web requests. Learn more: 🔗 go.dhs.gov/5Hi
Cesar Chavez Martinez retweeted

🔴 Araştırmacı @4osp3l, Microsoft Azure Application Gateway v2 üzerinde ilginç bir 403 Forbidden bypass yöntemi buldu.
403 Forbidden veren bir URL, URL'nin sonuna "?x=.js" ekleyince (veya query string içinde .js geçen herhangi bir şey) kısıtlama bypass oluyor ve sayfaya erişilebiliyor.
Cesar Chavez Martinez retweeted

Hackers chinos espiaron a miles de empresas tras vulnerar la seguridad del gigante tecnológico ConnectWise.
techcrunch.com/2026/10/22/ch…


