

Secure, Scalable & Compliant DevSecOps, CyberSecurity, AI tooling, SRE & FinOps Solutions. Connect via https://teapaw.org/t.co/CaUilu5rdL or email for a consultation.
Bengaluru, India
Joined May 2015
- Tweets620
- Following422
- Followers43
- Likes3.1K




ProDevOps retweeted

This is the state of security in India, largest broker @zerodha with AUM of around $60B offers whopping $1.5k for a P1 bug report, can you imagine?
Just now CBSE, largest and government owned education department leaked all the data and when @ni5arga reported they did not bother.
Sometime ago (2 years) I found a bug in some government medical website with which EVERY SINGLE INDIAN who ever used government services, their blood report can be accessed with just mobile number, I went out of my way to ping all the associated people on linkedin, emails and everything, but 2 years later it's still live.
Now people + gov will try to hunt down/ put cases on this kid for reporting issues publicly.


I had hacked CBSE's OSM (On-Screen Marking Portal) in February and had reported the vulnerabilities to CERT-In, but they were unable to patch most of them.
I've written a detailed blog post about it here: ni5arga.com/blog/posts/hacki…

ProDevOps retweeted

Do you guys want to know how the biometric system is bypassed/ hacked? It's ingenious. I know it because advised on one such case.

How do you stop exam paper leaks? A tech- based reform required.
Under the leadership of DGP,Haryana, Sh. Ajay Singhal — an innovator and reformer in policing — Haryana Police rebuilt the B1 promotion exam from scratch. Zero paper. Zero human contact. Zero leaks.
Between 2018-2024: 7 exams | 34,278 constables appeared | 14,000 unique question papers | Each candidate got a different set of 140 Qs | Instant email results | CCTV + biometric + firewalls.
Result: Zero cheating. Zero litigation.
First police force in India to do this.
“Every leaked paper is a letter of rejection to fairness.” - DGP Ajay Singhal
When will, planning & technology combine, trust is restored. This is how you dismantle the exam mafia.
#TechForTrust #HaryanaPolice #ExamReforms #DGPInitiative
#PoliceReforms
#Fairness
#TribuneCHD
@cmohry @NayabSainiBJP @csharyana @DgpChdPolice @dgpup @DGPPunjabPolice @dgpapofficial @DGPMaharashtra @CPDelhi @thetribunechd @htTweets


Indeed.
Anyone trying to get into Cybersecurity business in India must know this basic fact, before losing their sanity, time and money.

12
Most of those "empanelled" firms end up being spokespersons of the establishment, only to retain their empanelment status, and safeguard their contracts & revenue.
Real cybersecurity situation with most institutions & firms in India is unbearably uncomfortable. And nobody cares.

I once criticized CERT-In on LinkedIn and got calls from terrified employers (past & then present) asking me to remove it.
I said no and proceeded to change all my employment history to ‘Confidential’ to ease their worries.
The reason they panic is because they don’t want to lose their “CERT-In Empanelment”.
CERT-In Empanelment is one of the biggest scams in the Indian cyber security industry.
CERT-In makes you go through several stages of tests (all worthless btw) and then “certifies” you as an empaneled auditing firm.
This status then allows you to bid on government contracts for cyber security projects along with enabling you to serve compliance customers under regulatory bodies.
If, for whatever reason, CERT-In decides to revoke this empanelment, the firm would lose majority of its business.
That’s how CERT-In keeps all the major cyber security firms in India under their thumb.
1
40
Prima facie, details posted by @ni5arga seem valid.
Bigger concerns:
1. no competent private firm would validate, as they fear retribution by GoI, impacting business/revenue
2. many competent independent researchers have seen GoI filing criminal cases, just to silence them

11
ProDevOps retweeted

A new generation of people are realising how messed up CERT-IN and India's cybersecurity is.
ProDevOps retweeted

I once criticized CERT-In on LinkedIn and got calls from terrified employers (past & then present) asking me to remove it.
I said no and proceeded to change all my employment history to ‘Confidential’ to ease their worries.
The reason they panic is because they don’t want to lose their “CERT-In Empanelment”.
CERT-In Empanelment is one of the biggest scams in the Indian cyber security industry.
CERT-In makes you go through several stages of tests (all worthless btw) and then “certifies” you as an empaneled auditing firm.
This status then allows you to bid on government contracts for cyber security projects along with enabling you to serve compliance customers under regulatory bodies.
If, for whatever reason, CERT-In decides to revoke this empanelment, the firm would lose majority of its business.
That’s how CERT-In keeps all the major cyber security firms in India under their thumb.
Okay this is __HUGE__!!!
ni5arga.com/blog/posts/hacki…
Hey @ni5arga, can you open your DM please!
20
Well, pam_fingwit has a pretty easy LPE bug.
github.com/xapp-project/fing…
(Security issue: Local Privilege Escalation in pam_fingwit)
This one needs physical access to the machine, but the impact is way too high!

1
1
56
If you are using an ISP other than Airtel or Jio in India, your Ecovacs robot might not be able to reach ecovacs.com due to buggy filtering at Ecovacs portal, thus rendering your robot unuusable.
Issues started after 24Mar2026.

Hey @ecovacsrobotics, @excitel_rocks
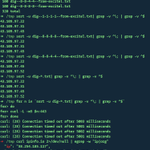
ecovacs.com (resolves to all.ecovacs.com.a1.initww.co…) isn't reachable from a few ISPs like Excitel in India.
Excitel resolves that to 43.109.97.45 & times out, whereas Airtel resolves to 155.102.2.162 & works.
Check your DNS!

51
ProDevOps retweeted

You can now run a full Linux operating system inside a 6mb PDF.
Someone embedded a RISC-V emulator inside a standard document. You don't need a virtual machine, just a PDF reader.
→ Runs interactively inside the file.
→ Powered by a tiny RISC-V emulator.
→ The entire OS fits in just 6MB.

ProDevOps retweeted

Mercor AI has allegedly been breached by Lapsus
939GB of source code
4TB of data in total
All data from their TailScale VPN
@mercor

ProDevOps retweeted

SOMEONE DROPPED A FULLY JAILBROKEN, OPEN-SOURCE, PRE-BUILT IOS 26 VIRTUAL MACHINE
Repo: github.com/34306/vphone-aio

Readers added context they thought people might want to know
The "someone" who released this is @Little_34306 (as seen on the linked GitHub: github.com/34306). The OP regularly fails to credit the work they post.
ProDevOps retweeted

PSA: If you've been running out of Claude session quotas on Max tier, you're not alone. Read this.
Some insane Redditor reverse engineered the Claude binaries with MITM to find 2 bugs that could have caused cache-invalidation. Tokens that aren't cached are 10x-20x more expensive and are killing your quota.
If you're using your API keys with Claude this is even worse. This is also likely why this isn't uniform, while over 500 folks replied to me and said "me too", many (including me) didn't see this issue.
There are 2 issues that are compounded here (per Redditor, I haven't independently confirmed this) :
1s bug he found is a string replacement bug in bun that invalidates cache. Apparently this has to do with the custom @bunjavascript binary that ships with standalone Claude CLI.
The workaround there is to use Claude with `npx @anthropic-ai/claude-code`
2nd bug is worse, he claims that --resume always breaks cache. And there doesn't seem to be a workaround there, except pinning to a very old version (that will miss on tons of features)
This bug is also documented on Github and confirmed by other folks.
I won't entertain the conspiracy theories there that Anthropic "chooses" to ignore these bugs because it gets them more $$$, they are actively benefiting from everyone hitting as much cached tokens as possible, so this is absolutely a great find and it does align with my thoughts earlier.
The very sudden spike in reporting for this, the non-uniform nature (some folks are completely fine, some folks are hitting quotas after saying "hey") definitely points to a bug.
cc @trq212 @bcherny @_catwu for visibility in case this helps all of us.


ProDevOps retweeted
Ironic how Anthropic sells Claude Code security reviews positioned as something v powerful (costing $15-25 per PR review), and being clear they use it on all PRs... then leaking all of Claude Code's code thanks to publishing their sourcemap.
AI won't save you from yourself!
It's sorta amusing to find that many are discovering now that version-pinning* is a great way to save oneself from cybersec disasters.
*was once an almost mandatory thing, in places with a decent safety-first programming culture, at least till 2015.
ZIRP & YOLO era ruined it!😂

Today is another package-lock.json appreciation day!
- Make sure you always commit your project with the package-lock.json file. It is the ONLY version locking enforcement mechanism.
- Use npm ci instead of npm install. The first one will work ONLY if package-lock.json exists.
- If you need to update or pull new packages, use the --min-release-age flag (available since npm v11.10.0) to make sure you only install updates, which are at least 7 days old:
npm install --min-release-age=7
Or hardcode this setting into your .npmrc file:
min-release-age=7
There will be more malicious updates to popular npm packages in the future, driven by supply chain attacks. It's just the beginning.
Thankfully, they will be caught in the first 24 hours.
The npm ecosystem is broken by design.
Adapt and act accordingly.
Stay safe out there!

1
2
393
ProDevOps retweeted

🚨 ZERODAY: ImageMagick 🚨
Our autonomous pentester pwn.ai just dropped multiple zeroday chains in ImageMagick that achieve RCE and File Leak from a single .jpg or .pdf file, bypassing EVERY security policy (Default, Limited, AND Secure). 🤯
💥 Affects Ubuntu, Debian, WordPress & millions of servers globally. Happy Monday and Happy Hunting! 🥰
pwn.ai/blog/imagemagick-from…

ProDevOps retweeted

Holy shit… 4TB of job INTERVIEWS, RESUMES, and AI SECRETS just leaked from a $10 BILLION startup.
MERCOR uses AI to match people with high-paying gigs and literally records your face, voice, KYC docs and keeps it forever to “match” you with jobs.
Your FACE + VOICE + ID could be on the dark web right now.
Hackers (Lapsus$) claim they stole 4 TB through the company’s Tailscale VPN:
- 211 GB of candidate resumes and personal data
- Terabytes of video interviews + passport + KYC docs
- Almost 1 TB of source code
damn that Claude Mythos "God Tier" at Cyber stuff got into the wrong hands lol

Mercor AI has allegedly been breached by Lapsus
939GB of source code
4TB of data in total
All data from their TailScale VPN
@mercor
Claude finds an RCE in vim; older vim is immune!
Imagine an seeker who can run Claude against all popular FOSS, in parallel on their many used/popular versions, and build out a DB of exploits that work across many versions of an app.
Remember K3yM4k3r from Matrix Reloaded!😂


We asked Claude to find a bug in Vim. It found an RCE. Just open a file, and you’re owned. We joked: fine, we’ll switch to Emacs. Then Claude found an RCE there too.
Full story: blog.calif.io/p/mad-bugs-vim…

47