
zkVM, Rollup, Post-Quantum Cryptography CTO @ProjectZKM / @GOATNetwork Creator @AppliedPQC
worldwide
Joined July 2016
- Tweets1.3K
- Following684
- Followers968
- Likes2.5K






Pinned Tweet
Happy to share our latest work on Ziren @ProjectZKM @GOATNetwork. Feedback welcome!
A summary:
1. A new proof system based on Jaggled reduction and WHIR(including recursion proof over binary field and Blake3). Acknowledgements to SP1 team and Plonky3 contributors.
2. 4x proving efficiency, 10x emulation efficiency improvement over previous v1.2. Speedup is happening every day with AI assistant.
3. >100-bit proven security
4. A fully Lean 4 assisted constraint determinism proof, covering 104 chips.
5. A complete end-to-end zkVM design reference.

[New] Ziren: Succinct Arguments for MIPS32 Execution (Stephen Duan) ia.cr/2026/2330
Make zkVM and Bitcoin Rollup technology for daily life!

Good thread.
One data point on depth, from our Ziren paper (eprint.iacr.org/2026/2330):
Our recursion is not open-ended (unlimited depth). A block proof is one leaf per shard, a compose tree of arity ≤ 3, and a single root: depth 2 + ⌈log₃ N⌉, about 7 levels for our largest test block. The recursion keys are not inputs either. Every leaf and compose key must sit in a fixed allowlist committed under one root, and the verifier fixes the schedule rather than reading it from the proof. That's a bounded, closed set of verifier circuits, a different risk profile from unlimited-depth recursion with the aggregated vk passed in as input.
We also state the recursion assumption as an open hypothesis rather than a belief. Our composition theorem works in the ROM, where Fiat–Shamir costs log(Q) bits for Q oracle queries: a 150-proof tree has 93.51 interactive bits, 53.5 at Q = 2^40. It holds under hypotheses including that "each node's extractor succeeds on the transcripts its parent's extractor produces".

A few reflections on the lattice vs. hash-only debate that our recent Aerie post sparked:
1. Cryptographic ossification for blockchains was never safe. Until the day we know with certainty that P ≠ NP, that finding short vectors in lattices is intractable, that Keccak effectively behaves like a random oracle in deployed SNARKs, and that every single bug has been eliminated from our codebases, blockchains cannot ossify. That is simply not how safe systems are built. Issues will arise, and the system will have to respond.
It’s a double standard to reject lattices because blockchains are hard to upgrade if lattices break, while counting on upgrades if AI breaks your hash function or finds a critical zkVM bug.
The best counterargument is that hash-only designs are more agile: if your hash function breaks, just swap out the hash. But we must aspire to a higher level of agility than this. Indeed, as I cover next, if SNARK recursion itself turns out to degrade security, the proposed hash-only blockchain designs would need to be rethought from the ground up.
2. The real security debate is not lattices vs. hashes — it is lattices vs. building everything on SNARK recursion. That’s because “hash-only” is not really hash-only: it rests on hashes plus the soundness of deep SNARK recursion. Ethereum’s roadmap relies on exactly that: hash-based aggregation needs recursion to keep up with a slot’s worth of signatures, and EIP-8288 would send other signature schemes and users’ own proofs through the same recursive pipeline. In contrast, Aerie proves a slot’s worth of signatures on one laptop without any recursion.
All deployed post-quantum SNARKs rely on the Random Oracle Methodology (via Fiat–Shamir) to establish their security. This is an idealization we know fails in the real world: we have explicit counterexamples where “SNARKs” coming out of this methodology are totally insecure when instantiated with any concrete hash function.
We generally ignore these counterexamples in part because they only arise when proving contrived, self-referential statements about the very hash function used by the SNARK verifier.
But proving statements about the verifier’s own hash function is the exact thing you do in SNARK recursion. That’s why the security of recursive SNARKs can’t be established even in the random oracle model.
On top of that, the standard security proofs for recursion (in other models) suffer an “extractor runtime” blowup that is exponential in the recursion depth, suggesting that security may degrade as more recursion is applied. Yet Ethereum’s own EIP-8288 enables unlimited-depth recursion, even as it lists soundness of recursive SNARKs as a trust assumption. Proofs in more idealized models avoid the blowup, but they mainly tell us that an attack on SNARK recursion would have to exploit the concrete hash function, which is exactly what the Fiat–Shamir attacks above do.
To be clear, we don’t know of any outright attacks on SNARK recursion, and I very much hope it is secure. But some of us who have studied the question have a lingering sense that an attack may be possible in some settings. And if AI is going to supercharge cryptanalysis, there is no reason to expect it to spare Fiat–Shamir for SNARKs, let alone SNARK recursion, both of which have had far less scrutiny than lattices.
So, I do not concede that a “recursion everywhere” hash-only approach is clearly more conservative than one built on standard lattice assumptions.
3. “Just wrap everything in a hash-based SNARK” (like EIP-8288) faces challenges.
Aggregating signatures and proofs off-chain into a single block-level proof is a powerful design independent of the hash-only vs. lattice debate, and I am not telling people to avoid it. But claiming, as Vitalik Buterin did this week, that users can run whatever cryptography they want locally and wrap it in a client-side leanVM proof glosses over major hurdles.
For example, leanVM today is a minimal VM designed almost entirely to prove hash-based signatures and recursion, not general-purpose computation. And binary-field SNARKs like leanVM remain slow at proving the integer multiplications that lattice cryptography does en masse.
I am optimistic that many of these zkVM challenges can be met (including via my own work, binary-field Twist and Shout, which are now implemented in Magnetar). But regardless, if lattices can make aggregation simpler and faster, then they should be leveraged. We need to be agile no matter what.
4. For chains whose reason for existence is privacy, I truly struggle to understand the pushback. Public-key encryption (and fast single-server PIR) cannot be built from hashes alone, at least not in any black-box way. If lattices break, it is going to be very, very hard for these chains to provide acceptable levels of privacy and functionality. For a project whose entire reason for existence is privacy, a loss of confidentiality is an existential failure. Next to that, a second signature upgrade (after the first one, from elliptic curves alone to, hopefully, a hybrid lattice scheme) is easy.
Summary: We don’t know for sure what is secure and what isn’t. We are all weighing unquantifiable risks against each other, and we do not need to agree on a total order on them. But hash-only solutions face many open engineering challenges, and they are not more “conservative” in the way some have argued. Some of those challenges are entirely prosaic and have nothing to do with bugs or cryptography, like hardware support for custom schemes whose hash function is still undecided. I hope we can overcome those challenges within the appropriate timelines, but they must be acknowledged and portrayed realistically.
Overall, cryptographic agility and defense in depth (e.g., hybrid signatures) are the answer, which is why we are building both lattice-Jolt and hash-Jolt. In practice, the positions are less polarized than social media discourse suggests: for example, StarkWare is working to make Falcon verification cheap (falcon.provably.fast/), which is great to see.
Here is the (apparently) controversial take I am sticking to: Conditioned on agility, whenever lattices make systems simpler or more functional, we should embrace them rather than default to “hash-only” designs. Lattices are what the rest of the world will depend on, with decades of study and hardening behind them, and at the system level, less functional often means less secure. Where hash-only designs are just as simple and functional, by all means use them.

And another ongoing part is our BitVM bridge. We have finished the phase 1 prototype, with recursion proofs of WHIR on binary field and Blake3, we have reduce the proof size to 69KiB, and make it pragmatic to verify a WHIR Proof on Bitcoin via BitVM+ Garbled circuit. On phase 2, we are trying different techniques to reduce the onchain materials(proofs, OTS, and verification scripts).
Those two are the most important things to make @GOATNetwork become quantum resistant.
Nobody knows exactly when today’s cryptography gets broken by a quantum computer. What matters is that the quantum-resistant replacements are running before it does.
On GOAT Network, validator consensus keys are moving from secp256k1, the signature curve most chains use today, to ML-DSA-65, one of the NIST post-quantum standards.
The full post-quantum picture can be found at goat.network/news/a-post-qua…
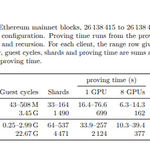
Share some numbers about multi-client proving for Ethereum with Ziren V2.0 @ProjectZKM, which can prove 75.8MHz with 8X5090, and 12MHz with 1X5090.
And the instruction efficiency of Geth/Reth is around 7x, which seems larger than 5 months ago, because we did more guest side optimizations on Reth:
> Witness and trie: arena nodes, compact digest references, borrowed input slices, faster RLP decoding, and fewer allocations and clones.
> Memory and hashing: word-wise comparisons, a cheaper hash-map hasher, and Keccak input buffers built directly, using the stack for short inputs.
> 256-bit arithmetic: multiplication and modular multiplication use zkVM precompiles; division uses hints checked inside the guest.
> Cryptography: syscall-backed BN254 and BLS operations, cached KZG preparation, and accelerated modular exponentiation.
> EVM interpreter: MIPS32 fast paths for gas accounting, stack swaps, and memory loads/stores.
PS. the number in the picture will be updated in our next release of our paper.
@go_ethereum @ethereumfndn


Happy to share our latest work on Ziren @ProjectZKM @GOATNetwork. Feedback welcome!
A summary:
1. A new proof system based on Jaggled reduction and WHIR(including recursion proof over binary field and Blake3). Acknowledgements to SP1 team and Plonky3 contributors.
2. 4x proving efficiency, 10x emulation efficiency improvement over previous v1.2. Speedup is happening every day with AI assistant.
3. >100-bit proven security
4. A fully Lean 4 assisted constraint determinism proof, covering 104 chips.
5. A complete end-to-end zkVM design reference.
Fully agree!
AI is speeding up the break of traditional hardness assumption/construction, meanwhile AI is also improving the security of blockchain infrastructure, from software formal verification, active realtime defense, code robustness, most importantly, to the upgrade and adoption of post-quantum cryptography.

Can't agree with this more. No matter whether the attacks from PQ or AI, serious crypto projects are always placing more attentions to application of cryptography, more secure parameters, more advanced protocols.
when i create @appliedpqc, the first co-author is a phd from Communication Security, and we also did lots of research on the TLS related PQ updates.

I've read this post 5+ times and I increasingly have trouble with the core point.
If ECDSA breaks without warning, we have so much more to worry about than our magic internet money. Internet security as a whole is gone. SSL/TLS gone, the internet is now transparent.
Not just internet security as well - a large portion of physical security would become irrelevant too. You can't have secure digital locks if encryption is dead. You can't secure surveillance footage if the gateway it's stored on can be wiped out on a whim.
We would have much bigger problems than "your magic internet money gets stolen." The floor would drop out of the global economy.
Most importantly - the answer to transparent encryption simply cannot be "hide your magic internet money" when the internet wouldn't exist anymore. You'd be relying on this technology coming back online, and not just that, you'd be relying on the tokens you stashed away being the relevant ones when it does.
I get the ~reasonable dooming here, but if we're going to doom you have to take it to its conclusion. You're going to be much better off investing in gold or cylindrical lead if your core hypothesis is "ECDSA could be broken within months"
zkAPI is an anonymous prepaid authorization protocol.
More like an anonymous "openrouter"


Really impressive clip! @GOATNetwork

Stephen Duan retweeted

The GOAT CEO is on the @KBWofficial stage right now, and he has one mission: help your business get ready for the agent economy.
@KevinLiu, live on the Stable Stage 🇰🇷


ZK does not remove trust while what ZK is good at is narrower, and more useful. It can prove one fact, age, wealth etc., not on a sanctions list, without handing over the passport, address, or income behind that fact.
It changes what you have to trust. Today’s KYC/AML model treats a full identity file as proof of compliance. Every institution collects the same personal data, stores it, and hopes a bigger database will catch more crime. That is the “data haystack”: more records, more breach risk, not necessarily more signal.
But the trust root remains. A proof only shows that some inputs satisfy a rule. It does not prove those inputs were honest. Someone still has to issue the credential, screen the wallet, or sign the risk score. If that issuer is compromised, the math will still verify a bad claim.
So the real world stays responsible for issuance and accountability. ZK keeps disclosure small, the chain stores a checkable proof instead of a personal file.
ZK can shrink the haystack. It cannot certify the needle.
#zkvm


Stephen Duan retweeted
KBW 2026 Giveaway! 🇰🇷
One of the perks of being a Diamond Sponsor of @KBWofficial is having tickets to give away to the GOAT community.
Two winners each get two: one for you, one for whoever you're bringing to Seoul.
To enter, answer one question in the replies: Your agent has your wallet. What's the first thing you wish it could purchase or do?
The best two answers win.
Follow us so we can DM you the tickets. Entries close on the 25th, and you'll need to get yourselves to Walkerhill, September 30th to October 1st.

I can understand AI is distilling everyone, and deprive us of innovation, curiosity, and execution, then people may feel pessimistic of privacy.
my point is actually opposite. AI is always the tools to improve people happiness and efficiencies.
The only changes is personal OPSEC(Operations Security) is approaching zero marginal value. From here, privacy is either a default property of the system — or it is mostly gone.

It's only dead if you give up
I'm not giving up on privacy. I'm doubling down.
firefly.social/post/x/210138…


Formal verification becomes one of the fundamental feature of proof system. Ziren 1.x @ProjectZKM was formally verified by Veridise, and the upcoming 2.0 is already formal verified by Lean4.

Thanks to Tachyon's @MariusMargulus, the new zk-SNARK prover in Zakura (and also in @vizorwallet) is the first Zcash prover with a machine-checked Lean proof of statistical honest-verifier zero-knowledge.
Read more:
zakura.com/engineering/ironw…

Understand SHRINCS - the first #Bitcoin PQ safe signature proposal - from the scratch.
GOAT Research has published a full explainer of SHRINCS, the draft signature scheme proposed for Bitcoin's post-quantum migration.
SHRINCS was published as a BIP in August. It is built from hash-based cryptography older than Bitcoin, runs entirely on SHA-256, and asks the network to trust nothing it does not already trust. The open question is its statefulness: a SHRINCS key signs through a compact path that must track how many signatures it has produced, because reusing a slot makes forgeries possible, and when state is lost a stateless path takes over at a larger signature size. Compact signatures in exchange for new wallet complexity is the trade the proposal makes, and it is the substance of the discussion around it.
The explainer covers the mechanisms behind that trade: the two signing paths, the state rules, the signature budget, and how the August draft differs from the April specification.
hackmd.io/@goatresearch/HkOe…
